
Bot Detection API Integration: A Server-Side Checklist
Build a bot detection API integration around server verification, event binding, retries, webhooks and an explicit policy before a protected action completes.
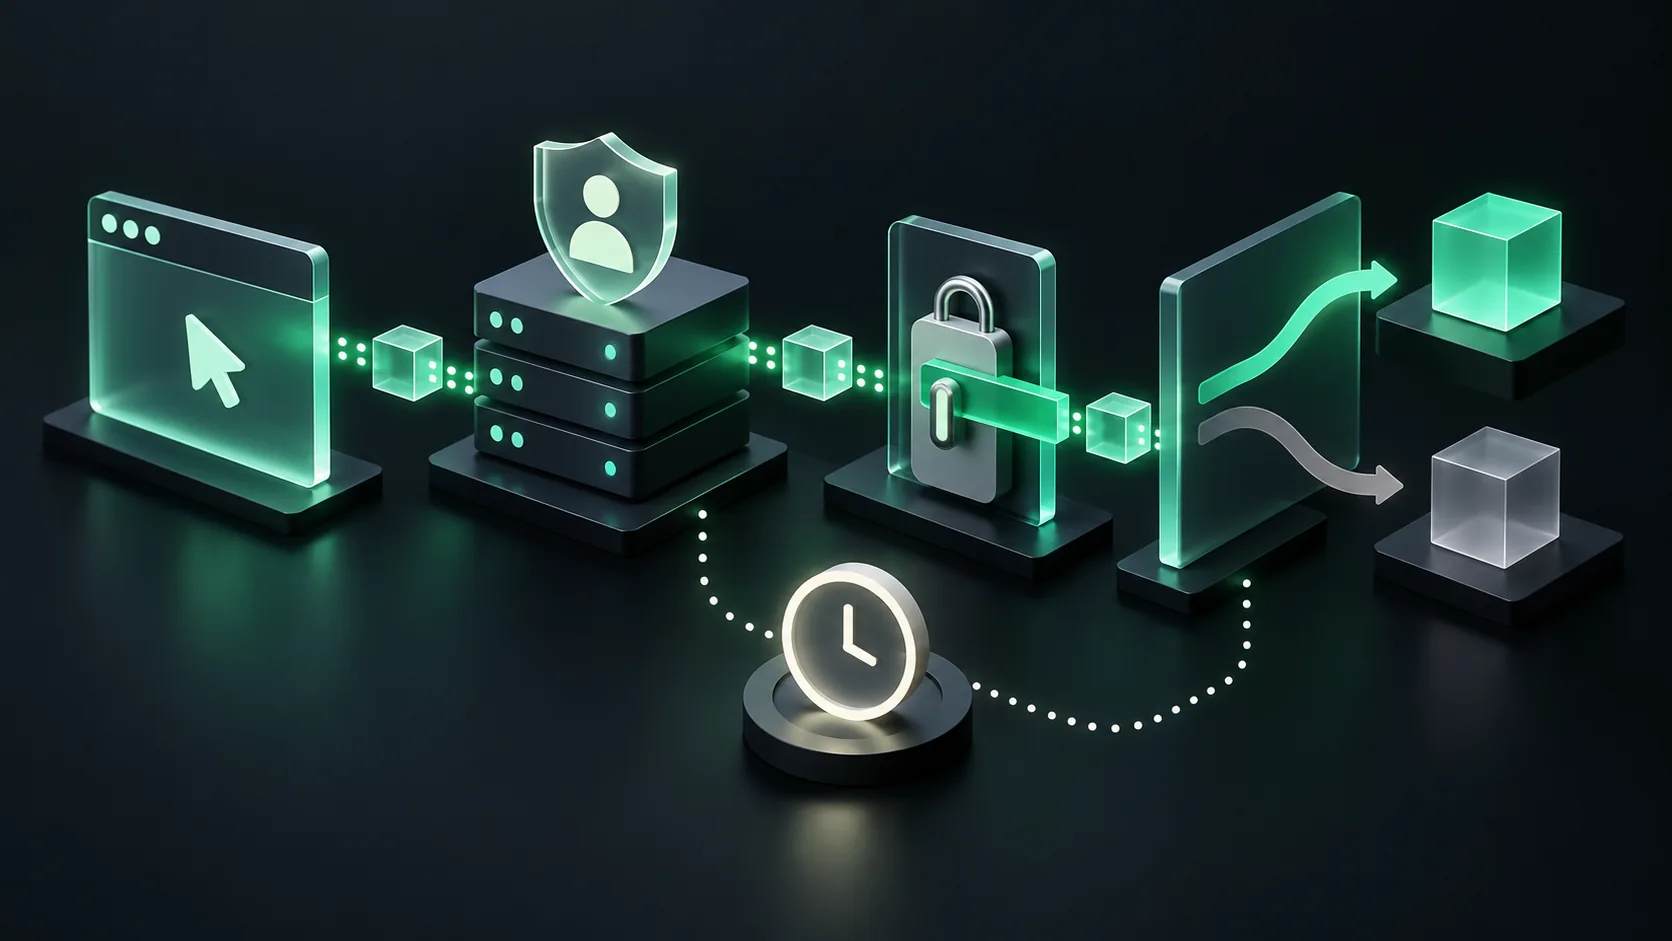
A bot detection API integration connects an observed interaction to a server-side decision before the protected action completes. The application should bind the observation to its session and account, retrieve or verify the result, handle missing evidence, and record the action idempotently. A browser-reported success value is not a substitute for a verified backend result.
The first design choice is the action you protect: registration, login, a message send, a claim, checkout or delivery. That choice determines when evidence is useful and what a timeout may cost. Selecting an API before defining the action often produces a score that arrives after the relevant value has already been released.
Which boundaries should the integration contain?
Keep browser collection, result verification, policy and business state separate. The browser can obtain an event reference; your backend decides whether that reference belongs to the current action and what the verified result means. The provider's identifier and your application's idempotency key serve different purposes.
| Boundary | Responsibility | Test case |
|---|---|---|
| Browser collection | Start an observation at the intended checkpoint | Collection is blocked or interrupted |
| Server retrieval | Authenticate and read the correct result | An event belongs to another environment |
| Policy | Turn evidence into an allowed action | Evidence is incomplete or ambiguous |
| Business transaction | Grant, send or deliver at most once | A request is retried after a timeout |
| Reconciliation | Preserve later outcomes and corrections | A webhook arrives after a newer decision |
The ShieldLabs API overview and identification flow describe one provider's collection-to-result boundary. Use the bot detection API article as implementation context, then verify exact fields against the current reference.
What must the server verify before acting?
The server should authenticate provider calls, bind the observation to the current session and action, and enforce its freshness and reuse policy. Never accept a score merely because it arrived in a browser request. Keep private credentials out of client code and avoid exposing complete provider responses to callers who do not need them.
For a signup benefit, save the pending action before retrieval. A successful result can then complete that action once. A second submission with the same action identifier should return the recorded outcome rather than issue another benefit. A different event reference should not silently create a new entitlement for the same claim.
Distinguish the provider's event record from the application's authenticated account. Follow the Server API reference and the API key guidance, then inspect request logs for accidental credential or personal-data exposure. Examples must be adapted to the application's own authorization and storage model.
How should retries and timeouts work?
Choose the fallback before enabling enforcement. A low-cost read may proceed with monitoring, while an expensive benefit may wait for review or a later result. The right fallback depends on the action; a network error must not silently become either a clean verdict or a confirmed fraud verdict.
Bound retries by time and action state. If the user cancels, do not release value when a delayed result eventually arrives. If the operation already completed, a retry should not overwrite the decision or repeat a payment, message or credit grant. Preserve the event and request identifiers needed to investigate the sequence.
The error-handling reference separates collection failures from a completed observation. Our workflow guide explains why operational failure and suspected abuse require different recorded reasons. A useful pilot includes both kinds of case.
When should a webhook change a decision?
A webhook can notify the server that a result or account event changed, but its delivery is not the business transaction itself. Verify the signature using the provider's current instructions, retain the original message bytes where required, and record a delivery identifier or equivalent deduplication key.
Check whether the event describes an identification, an account association or a change to an existing state. A late account event may justify investigation without reversing a completed action automatically. Record which policy was applied and whether a reviewer or later event superseded the original decision.
The webhook reference and scored-identification event are the relevant sources for that provider. Avoid copying a signature algorithm or payload field from a different SDK version. For a framework implementation, use the SDK integration guide.
What should a rollout prove before blocking users?
Start with observation mode and a small set of representative actions. Inspect legitimate shared devices, privacy tools, accessibility needs, interrupted sessions and application retries alongside deliberate automated attempts. The goal is to verify the integration and policy, not merely to collect suspicious screenshots.
Record verified-result availability, decision latency, collection failures, review workload and whether each protected action completed correctly. Explain how outcomes were labelled. A provider's marketing accuracy figure is not a measurement of your deployment, and a successful lookup does not establish that the decision policy is appropriate.
Compare bot detection tools only after the checkpoint and enforcement boundary are clear. A challenge, an edge mitigation system and an event-risk API can be complementary. Ask each vendor what the application must still implement.
Frequently asked questions
Can the browser send the score directly to the backend?
It can send an event reference or other input, but the backend should verify the result through the provider's supported mechanism and bind it to the current action. Do not trust an unverified browser score as an authorization decision.
Is a retry the same as a new identification?
Not necessarily. A retry may concern retrieval, collection or the business transaction. Define the scope explicitly so that retrying a network request cannot duplicate a grant or replace a newer decision.
Should every timeout block the user?
No universal rule fits every action. Define a fallback based on the action's cost and reversibility, record the missing evidence, and test the policy with legitimate users as well as attack cases.
Does a verified webhook automatically authorize delivery?
No. It establishes the message's supported verification properties. The application must still check the event, account, action state, policy and whether delivery has already occurred.
Sources and editorial scope
This checklist explains integration responsibilities rather than claiming a completed deployment or a common vendor benchmark. ShieldLabs documentation is included as a project-portfolio source; exact contracts remain version-specific.
Further sources for bot detection api
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs documentation: JavaScript agent | Verify the endpoint, event or data model against the current version before writing enforcement code. |
| ShieldLabs documentation: check() | Verify the endpoint, event or data model against the current version before writing enforcement code. |
| ShieldLabs documentation: identify() | Verify the endpoint, event or data model against the current version before writing enforcement code. |
| ShieldLabs documentation: identifyOnInteraction() | Verify the endpoint, event or data model against the current version before writing enforcement code. |
| ShieldLabs documentation: load() | Verify the endpoint, event or data model against the current version before writing enforcement code. |
| ShieldLabs documentation: CDN snippet methods | Verify the endpoint, event or data model against the current version before writing enforcement code. |
| ShieldLabs documentation: Versions and availability | Verify the endpoint, event or data model against the current version before writing enforcement code. |
| ShieldLabs documentation: Changelog | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: AI Copilot | Understand what a reviewer can inspect and distinguish an interface observation from the backend decision. |
| ShieldLabs documentation: Errors | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: FAQ | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: Glossary | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: Acting on results | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: How ShieldLabs works | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: Quick Start | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: Rate limits | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: Webhook setup | Check this deployment boundary before assuming that collection, credentials or delivery are configured. |
| ShieldLabs documentation: Troubleshooting | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| Stop API abuse. | Read the provider-stated product or use-case scope; verify the selected integration before applying a policy. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


