
Fraud Detection API Integration: Frontend and Backend SDKs
Plan fraud detection API integration across browser frameworks and backend SDKs. Review runtime support, verified results, webhooks and application policy.
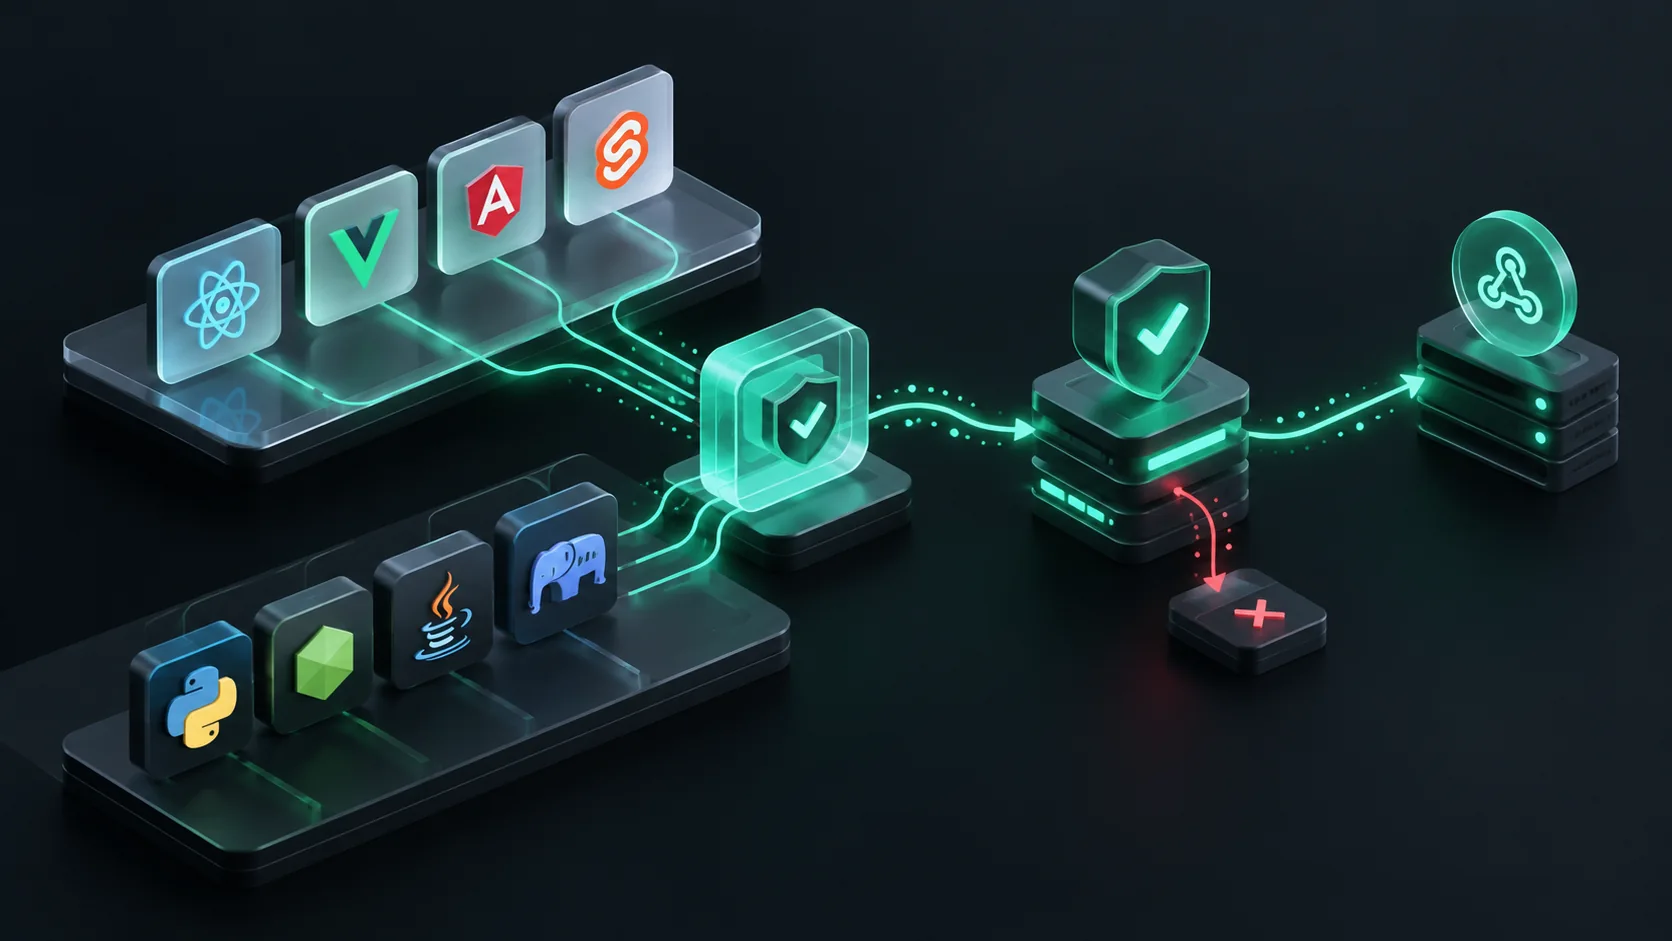
Fraud detection API integration usually needs both a collection path and an authoritative server path. Frontend SDKs help observe the interaction and obtain an event reference; backend SDKs help retrieve results and verify supported messages. The application still owns account binding, authorization, benefit state, retries and review. A framework wrapper does not move those responsibilities into the browser.
Choose packages by the actual deployment boundary. A server-rendered page, client component, background worker and webhook handler can have different runtimes and credential access. Document where code executes before following an example for a particular framework version.
How should frontend and backend responsibilities be divided?
A frontend integration should collect at a useful checkpoint and return the minimum reference the application needs. The backend should verify the result in the correct environment and connect it to its own authenticated action. Avoid serializing private credentials or a privileged client into page properties or public bundles.
| Layer | Typical job | Boundary to inspect |
|---|---|---|
| Browser SDK | Load collection and start an observation | Availability, consent configuration and lifecycle |
| Framework wrapper | Connect collection to component or route events | Client/server execution and repeated mounts |
| Server SDK | Retrieve results or verify supported webhooks | Secret management and runtime support |
| Application service | Apply policy and change business state | Authorization, idempotency and review |
The ShieldLabs SDK index and libraries page are useful starting points. They describe supported client and server packages. Confirm current versions and requirements before choosing an example; a tutorial for one framework version is not a compatibility guarantee for another.
Which browser framework paths should a team review?
Plain JavaScript, React, Next.js, Vue, Angular and Svelte integrations share an event boundary but differ in lifecycle. Decide whether collection starts at page entry, user interaction or the action being protected. Repeated component mounts must not silently create repeated business actions.
For a React application, keep collection state distinct from form submission state. For server-rendered frameworks, ensure code that requires browser capabilities runs on the client and that secrets stay on the server. A backend route should verify the submitted reference rather than trusting that the component rendered successfully.
Next.js deserves an explicit version check. Review the provider's Next.js setup against the framework version and runtime your application uses. An integration example with Server Actions is not automatically a working drop-in for every older App Router project.
What changes between backend languages?
Choose a server package that supports the runtime, response types and verification tasks you need. A synchronous web handler and an asynchronous worker may need different client patterns. Inspect timeout control, error surfaces, dependency requirements and how the SDK exposes the original response.
Node.js, Python, Go, PHP, Java and .NET can all participate in a collection-to-decision architecture, but package APIs are not interchangeable. Use the provider's language-specific reference, not a translated code sample with guessed method names. Keep the business action identifier independent from the provider's event identifier.
The server reference defines the underlying boundary. The data models help reviewers distinguish device, visitor, account and event fields. Our bot detection API checklist covers the application-level checks that remain after an SDK returns successfully.
How should WordPress, Laravel and an existing application differ?
Adding collection to an existing site is not equivalent to enforcing a risk decision. A WordPress snippet can observe an interaction while the application's signup, checkout or messaging logic remains elsewhere. A Laravel service can retrieve a result, but its route middleware and transaction still need a defined policy.
Use the WordPress integration discussion and Laravel guide to identify the relevant boundary. Separate edge request controls from browser evidence and backend account decisions. If an endpoint can release value without reaching the guarded path, protecting only a rendered form is insufficient.
For a gradual rollout, instrument one action, record the verified result and inspect whether the intended server handler uses it. Test direct requests, missing browser evidence and duplicate submissions. A healthy analytics chart does not prove that a bypassable endpoint is protected.
What should an integration test matrix include?
Write tests around behavior that can fail at a boundary: a result from another environment, a stale event, two submissions for one claim, an invalid webhook signature, a delayed message and a legitimate account on a shared device. Record the expected business outcome for each case before running it.
Inspect the development/production guidance and CSP setup. A collection script blocked by policy is an integration failure, not evidence that the visitor is malicious. Likewise, a supported browser list describes the provider's collection scope rather than every configuration in your customer population.
Keep the pilot result specific: framework, runtime, package versions, action, verification path and observed outcome. Do not describe an unrun code sample as tested. The vendor evaluation guide explains how to compare implementation work without turning one successful demo into a general performance claim.
Which SDK references and repositories match the application stack?
Use the setup guide to confirm the current package and runtime. The source repository is implementation material, not proof that a particular application integration has been tested. Browser and server roles remain separate.
| SDK | Role to inspect | Setup reference | Source repository |
|---|---|---|---|
| Angular | Browser framework | Angular setup | Angular SDK source |
| C#/.NET | Server retrieval and verification | C#/.NET setup | C#/.NET SDK source |
| Go | Server retrieval and verification | Go setup | Go SDK source |
| Java | Server retrieval and verification | Java setup | Java SDK source |
| JavaScript | Browser collection | JavaScript setup | JavaScript SDK source |
| Next.js | Framework client/server boundary | Next.js setup | Next.js SDK source |
| Node.js | Server retrieval and verification | Node.js setup | Node.js SDK source |
| PHP | Server retrieval and verification | PHP setup | PHP SDK source |
| Python | Server retrieval and verification | Python setup | Python SDK source |
| React | Browser framework | React setup | React SDK source |
| Svelte | Browser framework | Svelte setup | Svelte SDK source |
| Vue | Browser framework | Vue setup | Vue SDK source |
The ShieldLabs device-intelligence product reference describes the intended evidence layer. Use the SDK and server API contracts above to confirm how that layer reaches the protected application action.
Frequently asked questions
Does a frontend SDK authorize a protected action?
No. It helps collect evidence and obtain the provider's supported reference. Authorization and any change to business state remain responsibilities of the backend application.
Can a framework example be copied across versions unchanged?
Not safely by assumption. Check the provider's supported framework version, runtime and package APIs, then test the specific client/server boundary your application uses.
Is a webhook handler the same as the signup transaction?
No. Webhook delivery and application state changes are separate operations. Verify the message, deduplicate it and decide how it relates to the current action and any newer outcome.
What should be recorded when an SDK test fails?
Record the package and runtime versions, environment, action, failure boundary and expected outcome. Keep credentials and unrelated personal data out of the shared report.
Sources and editorial scope
The linked references describe provider-supported integration paths; they do not establish that RubyScore has deployed every package or tested every framework. ShieldLabs and its documentation are included as project-portfolio sources.
Further sources for fraud detection api
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs documentation: Build with AI | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: Integration | Understand what a reviewer can inspect and distinguish an interface observation from the backend decision. |
| ShieldLabs documentation: Integration glossary | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: Setup | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| ShieldLabs documentation: Domains | Check this deployment boundary before assuming that collection, credentials or delivery are configured. |
| ShieldLabs documentation: Connect through MCP | Check this deployment boundary before assuming that collection, credentials or delivery are configured. |
| ShieldLabs documentation: Where to integrate | Check this deployment boundary before assuming that collection, credentials or delivery are configured. |
| ShieldLabs documentation: Install the JS Snippet | Check this deployment boundary before assuming that collection, credentials or delivery are configured. |
| SSR Safe Angular Bot Detection: OWASP Layering and Server Validation | Background on Where Angular fits in a layered bot-management architecture. Verify implementation details in the primary references. |
| Browser Fingerprinting in a Python Web App | Background on What was checked in this example?. Verify implementation details in the primary references. |
| 4 Step Node.js Device Fingerprinting with W3C Privacy and ShieldLabs | Background on Why device fingerprinting helps and what it actually gives you in practice. Verify implementation details in the primary references. |
| Developers: Build Privacy First React Bot Detection With One JS Snippet | Background on Quickstart: adding CAPTCHA or attestation to a React form. Verify implementation details in the primary references. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


