
12 Best Bot Detection Tools for Signup and Login in 2026
Compare twelve bot detection tools by edge controls, browser evidence, challenges and account context, then test the endpoint and legitimate-user impact.
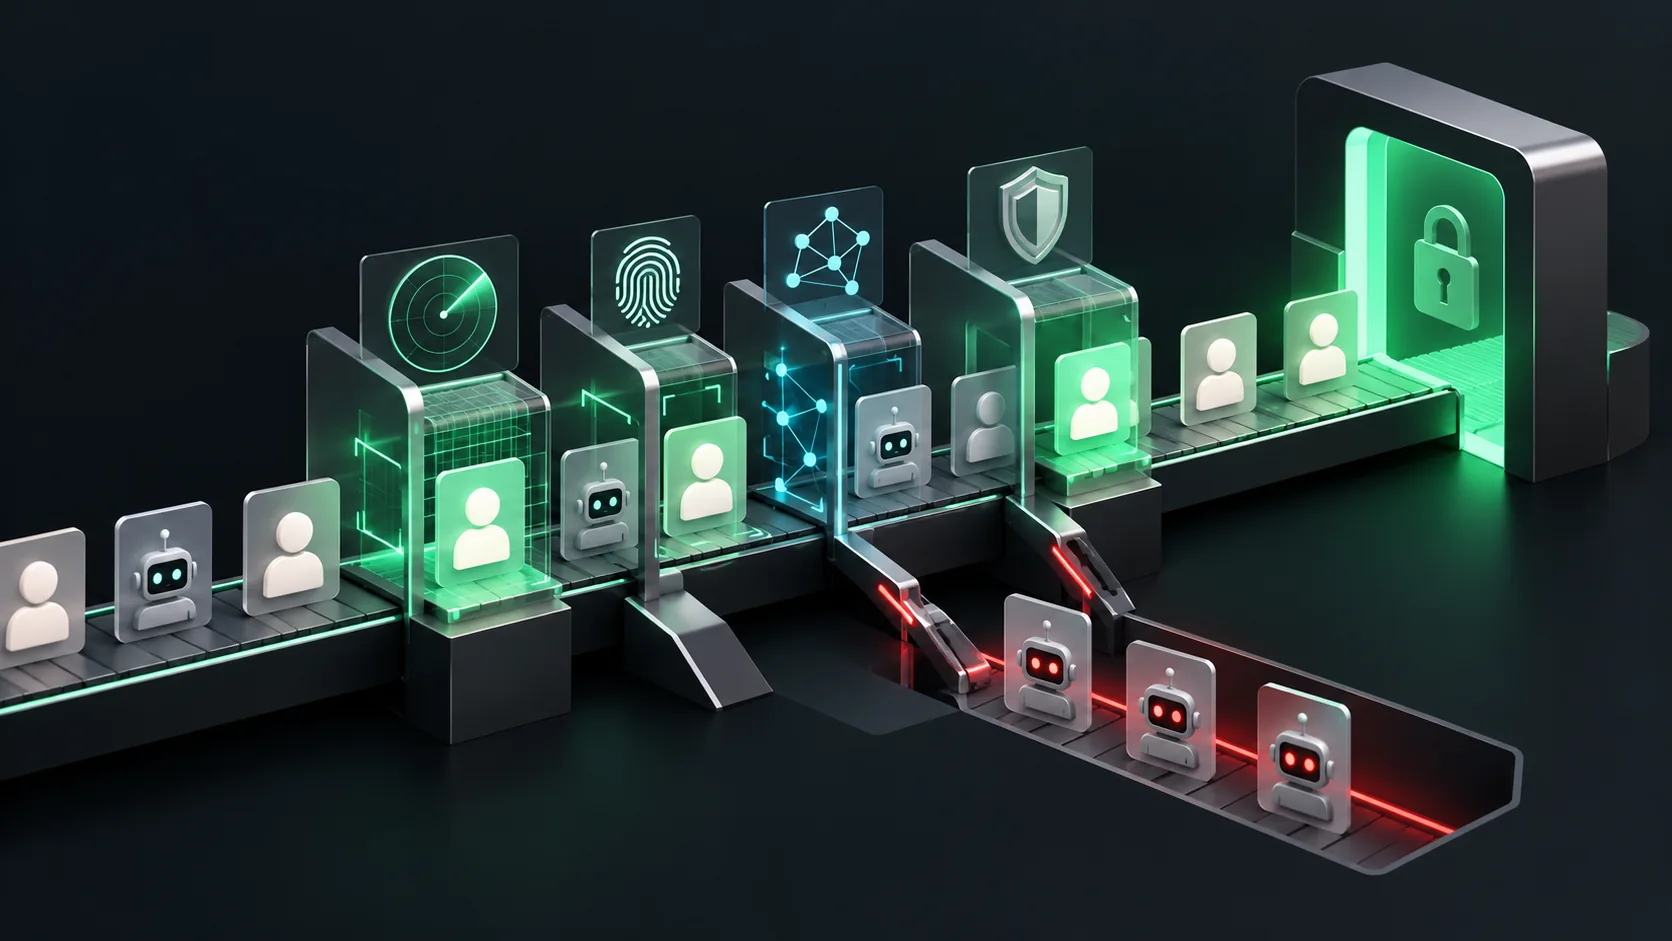
For signup and login, compare bot detection tools by where they observe and act. ShieldLabs and Castle connect automation with account context; Cloudflare, DataDome, HUMAN and Kasada address protected request paths; Arkose Labs adds adaptive detection and challenges. The useful shortlist depends on whether the loss is automated volume, compromised access or repeated account benefits.
A bot can be authorized, and a human-operated farm can violate eligibility rules. Your application therefore needs a policy for the action, not just a label for the client. A passed challenge is not proof that a person deserves another introductory credit.
The expanded shortlist includes different control layers. An identifier, an enrichment API, a challenge, an enforcement product and a business-policy engine are not interchangeable. Use the documented scope in the table to decide what to evaluate; inclusion is not a claim that every product detects every attack or fits every application.
What does this comparison cover?
This review, updated in 2026, covers documented deployment and response models. It does not measure a common catch rate or compare pricing without equivalent traffic and protection requirements. Check the products and integration paths currently available to your account.
Disclosure: ShieldLabs and related comparison publications are part of the project portfolio. Sources are attributed; no independent shared test is implied. Send factual corrections with the affected source to RubyScore.
Which bot tool fits the control point?
| Tool | Documented scope | Where it fits | What remains in your app |
|---|---|---|---|
| ShieldLabs | Device, network and account context | Teams connecting observed risk to an account action | Confirm the client SDK, server result contract and account-binding policy |
| Cloudflare | connect challenge and request policy | an automated request before a protected action | Account authorization and the action transaction |
| DataDome | Application bot protection | Teams protecting request paths affected by automated access | Verify endpoint coverage, decision availability and the separate account or entitlement policy |
| HUMAN | Application and advertising protection | Teams matching a specific HUMAN product to application or advertising risk | Name the selected module and validate its event and enforcement boundary before comparing outcomes |
| Kasada | Automation defense | Teams investigating automated interaction pressure | Confirm collection and enforcement coverage for the exact route and client used in the scenario |
| Arkose Labs | Adaptive interaction defense | Teams evaluating intervention when automated attempts reach an account checkpoint | Test challenge outcomes, legitimate-user handling and the account decision that follows verification |
| Castle | Application-event risk | Teams instrumenting explicit signup and login events | Check the event schema, score scale and policy response for the selected endpoint |
| SEON | Selected device and identity enrichment | Teams choosing several relevant evidence types for one decision | Confirm which modules, fields and account settings are included in the evaluation |
| IPQualityScore | Device and connection risk | Teams joining device and network findings to an owned workflow | Check the selected product, enabled features and server-side result retrieval path |
| Imperva Advanced Bot Protection | Automated traffic mitigation | Teams protecting relevant web or API request paths | Check integration placement, response options and the route for legitimate automated clients |
| F5 Distributed Cloud Bot Defense | Application bot defense | Teams assessing bot controls in a supported delivery architecture | Confirm the protected paths, deployment mode and operational handling of collection failures |
| Akamai Bot Manager | Bot management at delivery paths | Teams evaluating bot policy on supported application delivery paths | Review the actual integration, automation categories and intervention policy rather than assuming blanket blocking |
1. ShieldLabs: interpret bots in the account journey
ShieldLabs bot detection places automation evidence within a broader identification and risk view. Its usefulness for signup is the ability to review that evidence beside the account action rather than interpret automation in isolation.
Evaluate: whether a server-verifiable result arrives before access or credits are granted, and whether legitimate users with restricted browsers have a workable path. Compare confirmed repeated-benefit abuse separately from request automation.
2. Cloudflare: connect challenge and request policy
Cloudflare documents several challenge paths. The right configuration depends on which product handles the endpoint and the response required. Distinguish a challenge widget from the wider request policy around it.
Evaluate: endpoint coverage, origin bypass paths, challenge completion and retries. Logging a challenge response does not, on its own, connect the session to a valid account entitlement.
3. DataDome: protect the relevant application paths
DataDome Bot Protect describes automation protection for supported application surfaces. A useful evaluation maps each login, registration and API path to an actual integration rather than assume one protected website covers every client.
Evaluate: which legitimate clients need support, when an intervention occurs, and how the application records failed or abandoned challenges. Count operational handling as part of the cost.
4. HUMAN: examine the collection-to-enforcement architecture
HUMAN's detection overview describes a sensor, detector and enforcer. That architecture makes deployment coverage a concrete buying question: where are observations collected, and where is the response applied?
Evaluate: browser and server paths, missing client collection, permitted crawlers and the handling of interrupted sessions. Request risk should remain distinct from a conclusion about who owns an account.
5. Kasada: automation protection in an application stack
Kasada describes automated-threat protection and relationships among bot, device and account signals. A team should compare its integration against the actual attack path, including requests that do not follow the expected user interface.
Evaluate: deployment effort, client compatibility and observed outcome quality. Ask how the response affects a real user who returns after a network or software change, rather than compare only blocked attack traffic.
6. Arkose Labs: adaptive intervention in the flow
Arkose Labs' account-takeover material describes detection and adaptive challenges around access workflows. This is relevant when adding friction at selected points is part of the defense strategy.
Evaluate: challenge timing, completion and abandonment, accessibility, repeat attempts and recovery. A challenge can raise operating cost for an attacker while still needing separate account eligibility checks.
7. Castle: distinguish the bot score from account risk
Castle's risk-scoring documentation separates bot, account-abuse and account-takeover assessment. That separation can help an application use different policies for a registration attempt and a sensitive action after login.
Evaluate: the event context supplied and the application's response to each output. A legitimate session can still attempt an ineligible promotion, while an automated action may be permitted by product policy.
8. SEON: selected device and identity enrichment
SEON documents a modular Fraud API combining device information with selected IP, email, phone and other enrichment inputs.
Best fit: Teams choosing several relevant evidence types for one decision. Check before choosing: Confirm which modules, fields and account settings are included in the evaluation.
9. IPQualityScore: device and connection risk
IPQualityScore documents device identifiers, fraud findings and tracking variables that associate observations with user or transaction references.
Best fit: Teams joining device and network findings to an owned workflow. Check before choosing: Check the selected product, enabled features and server-side result retrieval path.
10. Imperva Advanced Bot Protection: automated traffic mitigation
Imperva describes advanced bot protection for distinguishing and responding to automated application traffic.
Best fit: Teams protecting relevant web or API request paths. Check before choosing: Check integration placement, response options and the route for legitimate automated clients.
11. F5 Distributed Cloud Bot Defense: application bot defense
F5 documents Bot Defense configuration and integration within its Distributed Cloud application-security products.
Best fit: Teams assessing bot controls in a supported delivery architecture. Check before choosing: Confirm the protected paths, deployment mode and operational handling of collection failures.
12. Akamai Bot Manager: bot management at delivery paths
Akamai describes Bot Manager as part of its application-delivery and automated-traffic protection portfolio.
Best fit: Teams evaluating bot policy on supported application delivery paths. Check before choosing: Review the actual integration, automation categories and intervention policy rather than assuming blanket blocking.
How do you run a useful signup and login pilot?
Evaluate separate endpoints before aggregating results. Login labels, registration labels and business-benefit labels are different. Otherwise, a large volume of blocked scripts can hide unnecessary challenges for a smaller but valuable customer cohort.
- Record the protected endpoint and allowed client types.
- Include ordinary users, restricted browsers and supported automation.
- Separate known malicious automation from unresolved traffic.
- Measure the result before and after the application policy.
- Reconcile account outcomes rather than call every flag a confirmed bot.
For an illustrative 500 legitimate logins, 10 unnecessary challenges represent a 2% challenge rate. A challenge abandoned by a user and one completed successfully have different impacts. Report both, with time-to-access and the sample definition.
The bot detection tools directory is supplementary reading. The ShieldLabs bot tools guide discusses additional selection context. A separate AI-crawler policy may also be needed; blocking every automated client can remove integrations a business intentionally supports.
Guides behind this comparison
For the underlying evidence and implementation questions, read Bot Detection: Tools, Signals and Campaign Eligibility and Click Farm Detection: Ad Fraud, Attribution and Payout Controls.
Frequently asked questions
Does passing a CAPTCHA prove an account is eligible?
No. It is evidence about a challenge interaction. Account history and the benefit rules determine eligibility, and a human-operated account can still violate those rules.
Is bot detection an account takeover solution?
It can address automated access attempts, but takeover can also involve human-operated sessions or recovery abuse. Evaluate authentication, account context and sensitive actions alongside request protection.
What should I compare besides a catch rate?
Legitimate-user impact, endpoint coverage, unsupported clients, missing results, review effort and completed business actions. A rate without labeled cohorts and a stated denominator is difficult to interpret.
Should I block all AI agents?
Define which agents and tasks your product permits. Verify identity where supported and enforce action limits. Automation and abusive behavior are separate policy questions.
Sources and editorial review
Reviewed on October 27, 2026 by RubyScore Research. Product descriptions are attributed to the cited documentation. Corrections can be sent to RubyScore.
[1] ShieldLabs bot detection — product documentation or the attributed publication above.
[2] Cloudflare — product documentation or the attributed publication above.
[3] DataDome Bot Protect — product documentation or the attributed publication above.
Further sources for best bot detection tools
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs research archive — page 11 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| ShieldLabs research archive — page 5 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| DataDome Alternative: ShieldLabs Comparison | Read this vendor-authored comparison as a source of evaluation questions, then verify the relevant product reference. |
| HUMAN Security Alternative: ShieldLabs Comparison | Read this vendor-authored comparison as a source of evaluation questions, then verify the relevant product reference. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


