
Bot Detection: Tools, Signals and Campaign Eligibility
Bot Detection: Tools, Signals and Campaign Eligibility. Compare evidence, practical controls and limitations, with related implementation sources.
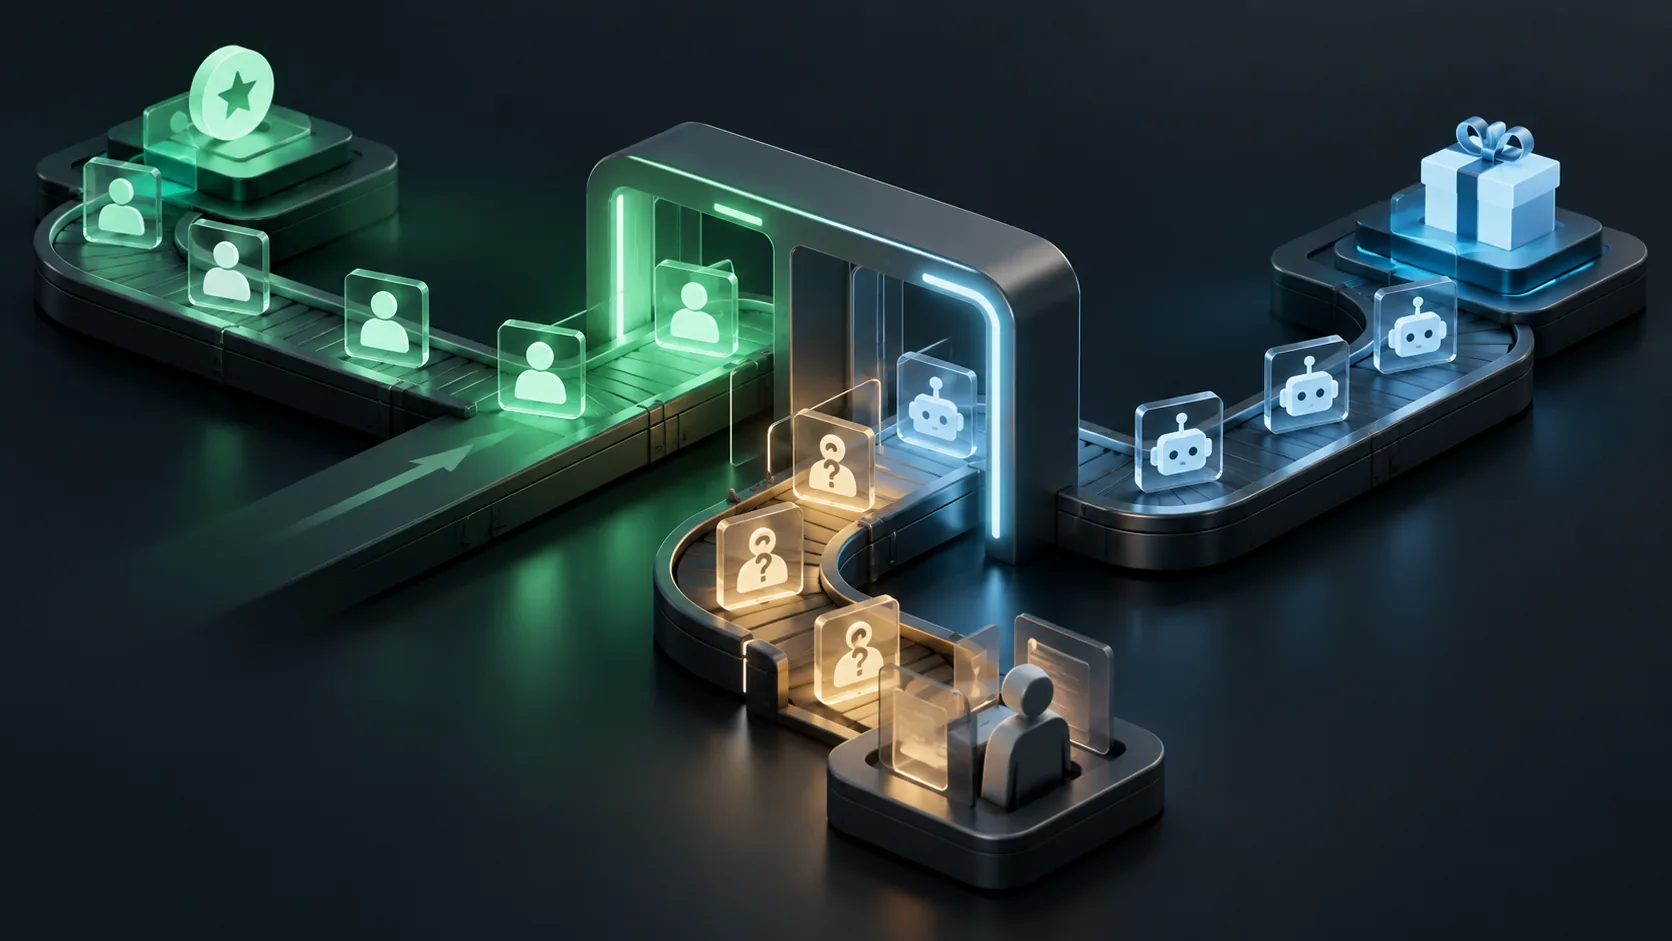
Bot detection assesses whether a request or interaction is automated. Tools can use browser, network and behavioral observations, but automation and abuse are different questions. Some bots are authorized, and human-operated accounts can still misuse benefits. Campaigns should combine the relevant bot result with account history and explicit eligibility rules.
This guide explains how bot detection works against crypto-native adversaries, why web2 defenses miss them, and how on-chain reputation separates real participants from mass-produced wallets.
What Is Bot Detection in Web3?
Bot detection is the process of distinguishing automated accounts from genuine human users. In web2 that usually means checking a browser session, a device, or an IP address. In Web3 the unit of identity is a wallet, not a session, so the same techniques do not transfer cleanly. A single operator can control thousands of funded wallets, pass every browser check, and still be one person running an airdrop farming ring.
The benefit of getting this right is direct: cleaner metrics, fairer reward distribution, and airdrop allocations that reach the users a protocol actually wants to keep. When quest-farming bots and sybil farmers dominate a campaign, real users receive diluted rewards and teams make roadmap decisions on inflated DAU (daily active users) figures.
How Bot Detection Works: Signals vs. Challenges
There are two broad families of bot detection, and Web3 leans heavily on the first.
- Signal-based detection observes behavior that already happened and scores it. On-chain, this includes transaction history, funding relationships, interaction timing, gas spend, and activity spread across chains. It is passive, hard to game at scale, and does not add friction for real users.
- Challenge-based detection forces an account to prove something in the moment: solve a CAPTCHA, pass a device check, or complete a proof-of-work puzzle. It is active and adds friction, and wallet-native bots often defeat it with cheap human-solver services.
The types of bot detection that matter for quests and airdrops are almost entirely signal-based, because the adversary controls the browser but cannot cheaply rewrite a wallet's entire on-chain past.
Types of Crypto Bots Mapped to Detection Signals
Not every bot is a farmer, and the right signal depends on what the bot is built to do. The table below maps common crypto bots to the signal that exposes them most reliably.
| Bot type | What it does | Strongest detection signal |
|---|---|---|
| Quest-farming bots | Auto-complete Galxe and Zealy tasks across many wallets | Identical interaction cadence, shallow transaction history |
| Airdrop farming rings | Operate thousands of wallets to capture allocations | Wallet clustering, common funding source |
| MEV bots | Front-run and sandwich pending transactions | High-frequency, contract-only interaction patterns |
| Arbitrage bots | Exploit price gaps across venues | Repetitive DEX routes, no consumer-style activity |
| Wash-trading bots | Trade against themselves to fake volume | Circular transfers between self-funded counterparties |
| Discord raid bots | Mass-join and spam community servers | Off-chain behavior; no wallet history behind the identity |
| Faucet drainers | Drain testnet and faucet rewards | Single-purpose wallets with no mainnet tenure |
Do crypto bots work? For their operators, yes: MEV and arbitrage bots are profitable trading tools, and farming bots reliably capture rewards when a campaign has no on-chain filter. That profitability is exactly why detection has to raise the cost of running them.
Why CAPTCHAs and Social-Stamp Checks Fail Against Wallet-Native Bots
CAPTCHA, reCAPTCHA, and hCaptcha verify a browser session, not a wallet. Farmers defeat them with low-cost human-solver services or headless automation while still controlling the wallets behind every quest submission. The check confirms that a human was present; it never proves that the wallet belongs to a distinct human. Social-stamp checks — a connected X account, a Discord role, an email — are just as easy to mass-produce.
Web2 bot management sits at the browser and network layer for good reason. Vendors like Cloudflare Bot Management, Akamai, HUMAN Security, and Fingerprint are strong at scripted web traffic, credential stuffing, and scraping. While a well-maintained roundup of bot-detection APIs is a useful starting point for filtering that kind of automated traffic, these tools inspect devices and requests, not on-chain identity. A farming ring can pass all of them and still be a thousand wallets funded from one address. How to avoid bot detection, from a farmer's perspective, is precisely this gap: solve the browser challenge, rotate IPs, and the wallets sail through.
On-Chain Behavioral Signals: Cadence, Clustering, and Protocol Tenure
The signals that actually separate humans from farms live on-chain, where history is costly to fabricate at scale.
- Interaction cadence. Farmed wallets complete tasks in near-identical time windows because a script drives them. Genuine users act on irregular, human schedules.
- Wallet clustering. Linking addresses funded from a common source, or that repeatedly move value in a ring, exposes coordinated operations behind superficially independent wallets.
- Protocol tenure. Real users accumulate a track record — swaps, bridging between chains, gas spent, and repeat interactions with protocols over months. A wallet minted the week of a campaign has none of it.
- Transaction diversity. Humans interact with many unrelated contracts; single-purpose wallets betray automation.
Best practices for bot detection follow from these: never rely on one signal, weight costly-to-fake history over cheap identifiers, and score continuously rather than gate once at signup. Layering signals is what makes evasion economically unattractive instead of merely inconvenient.
How to Detect Quest-Farming Bots on Galxe and Zealy
Galxe and Zealy are the dominant Web3 quest and campaign platforms, and both are heavy targets for farming. You can detect quest-farming bots on them because farmed wallets share observable patterns: near-identical task timing, shallow transaction history, funding from a common source, and no organic protocol usage outside the campaign itself.
The practical method is to cross-reference each quest completion against an on-chain reputation signal before rewards are distributed. A wallet that completed every task in the same five-minute block, holds no mainnet history, and was funded alongside five hundred siblings is not a distinct participant, regardless of how many social stamps it carries. Verifying whether an account is a bot, in this context, means checking whether the wallet's behavior is consistent with a human — not whether it can click a button.
Source: https://galxe.com Source: https://zealy.io
Analyze Existing Users for Bot Signatures, Not Just Raw DAU
Detection is not only a signup gate. Much of the value comes from re-analyzing the users you already have. Raw DAU counts every wallet equally, so a farming ring inflates the metric that teams use to judge product-market fit and campaign success.
Segmenting existing wallets by on-chain reputation reveals the real picture: how many active wallets show genuine tenure versus how many carry bot signatures. This lets a team block a bot's influence on allocations and analytics without punishing legitimate users, and it turns a vanity metric into an honest read on adoption. The benefit is decisions grounded in real engagement rather than manufactured activity.
Humanness Scoring and Proof-of-Human: The Costly-to-Fake On-Chain Layer
Humanness scoring quantifies how likely a wallet belongs to a real, independent human by aggregating on-chain signals into a single value. It weighs costly-to-fake behavior — transaction diversity, account age, gas spent, and activity across multiple chains — that automated farming rings cannot cheaply replicate across thousands of wallets. This is the layer that turns scattered signals into a decision.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
Bot Detection Tools vs. Building Detection In-House
Teams face a build-or-buy choice. Building in-house gives full control but requires indexing many chains, maintaining clustering heuristics as farmers adapt, and keeping pace with new evasion tactics — a standing engineering commitment. Adopting a reputation protocol or bot detection tools shifts that maintenance to a specialist and provides a portable score that works across ecosystems.
For most quest and airdrop teams, the pragmatic path is a hybrid: use on-chain reputation as the primary humanness filter, keep web2 bot management for browser-layer abuse, and reserve custom rules for protocol-specific edge cases. The measure of success is not a zero-bot campaign, which is unrealistic, but a cost structure where farming a reward is no longer worth the effort.
Bot detection tools, AI agents and CAPTCHA alternatives
The bot detection comparison directory provides additional product context alongside the application-specific checks below.
Bot detection tools should distinguish automation from prohibited behavior. Some crawlers and agents are authorized, and some abusive accounts are operated by people. Evaluate the endpoint, the permitted task and the evidence available before applying a challenge or block.
CAPTCHA alternatives include passive device and network context, account history, constrained workflows and action-specific verification. Each addresses a different failure mode. A passed challenge does not establish that a registration is entitled to another bonus; a bot flag does not establish that a crawler is unauthorized.
For implementation context, see bot and automation detection and AI-agent detection guide. Related editorial sources include Medium comparison of AI bot detection tools, Medium guide to betting-bot detection. Read next: best gaming fraud prevention tools 2026, browser fingerprinting techniques.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best Bot Detection Tools for Signup and Login in 2026.
Frequently Asked Questions
How do you detect bots in crypto?
You detect bots in crypto by analyzing on-chain behavior rather than page interactions. Effective methods combine wallet clustering (linking addresses funded from a common source), interaction-cadence analysis (identical task timing across accounts), and reputation scoring of costly-to-fake activity like swaps, bridging, gas spend, and protocol tenure across chains. CAPTCHAs and IP checks alone miss wallet-native bots.
Why do CAPTCHAs fail against Web3 bots?
CAPTCHAs verify a browser session, not a wallet, so farmers solve them with cheap human-solver services or headless automation while still controlling thousands of funded wallets. They add friction for real users while doing nothing to prove the wallet behind a quest submission belongs to a distinct human.
Can you detect quest-farming bots on Galxe and Zealy?
Yes. Farmed wallets share detectable patterns: near-identical task timing, shallow transaction history, funding from a common source, and no organic protocol usage outside the campaign. Cross-referencing quest completions against an on-chain reputation score separates mass-produced wallets from genuine participants.
What is humanness scoring?
Humanness scoring quantifies how likely a wallet belongs to a real, independent human by aggregating on-chain signals into a single value. It weighs costly-to-fake behavior such as transaction diversity, account age, gas spent, and activity across multiple chains that automated farming rings cannot cheaply replicate across thousands of wallets.
Can Web3 bots be detected reliably?
Bots can be detected, but no single signal is decisive. Reliable detection layers behavioral cadence, wallet clustering, IP and device data, and on-chain reputation. Because each layer raises the cost of evasion, combining them makes running a farming operation economically unattractive rather than only technically harder.
Is running airdrop or quest farming bots legal?
Automated airdrop and quest farming is generally not illegal, but it violates the terms of service of most quest platforms and airdrop programs, and detected wallets are routinely disqualified from rewards. For projects, the real cost is diluted allocations and inflated metrics, which is why on-chain bot detection is becoming a standard requirement.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] bot and automation detection — vendor product scope.
[2] AI-agent detection guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for how bot detection works
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs demo: Web Scraping Prevention Test | Inspect this controlled workflow example; do not treat a demo as a production accuracy benchmark. |
| ShieldLabs documentation: Web scraping | Use the scenario to plan an integration test; a published example is not a test result from your application. |
| Developer Playbook: Selenium Detection as a Five Signal Classification | Background on What Is Selenium Detection and Why Do Sites Use It?. Verify implementation details in the primary references. |
| ShieldLabs detection research archive | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| ShieldLabs detection research archive — page 2 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| ShieldLabs detection research archive — page 3 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| ShieldLabs detection research archive — page 4 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| ShieldLabs detection research archive — page 5 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


