
Cookieless Visitor Identification: Privacy and Consent
Review cookieless visitor identification through identifier scope, privacy choices, retention and deletion. Separate returning context from a verified person.
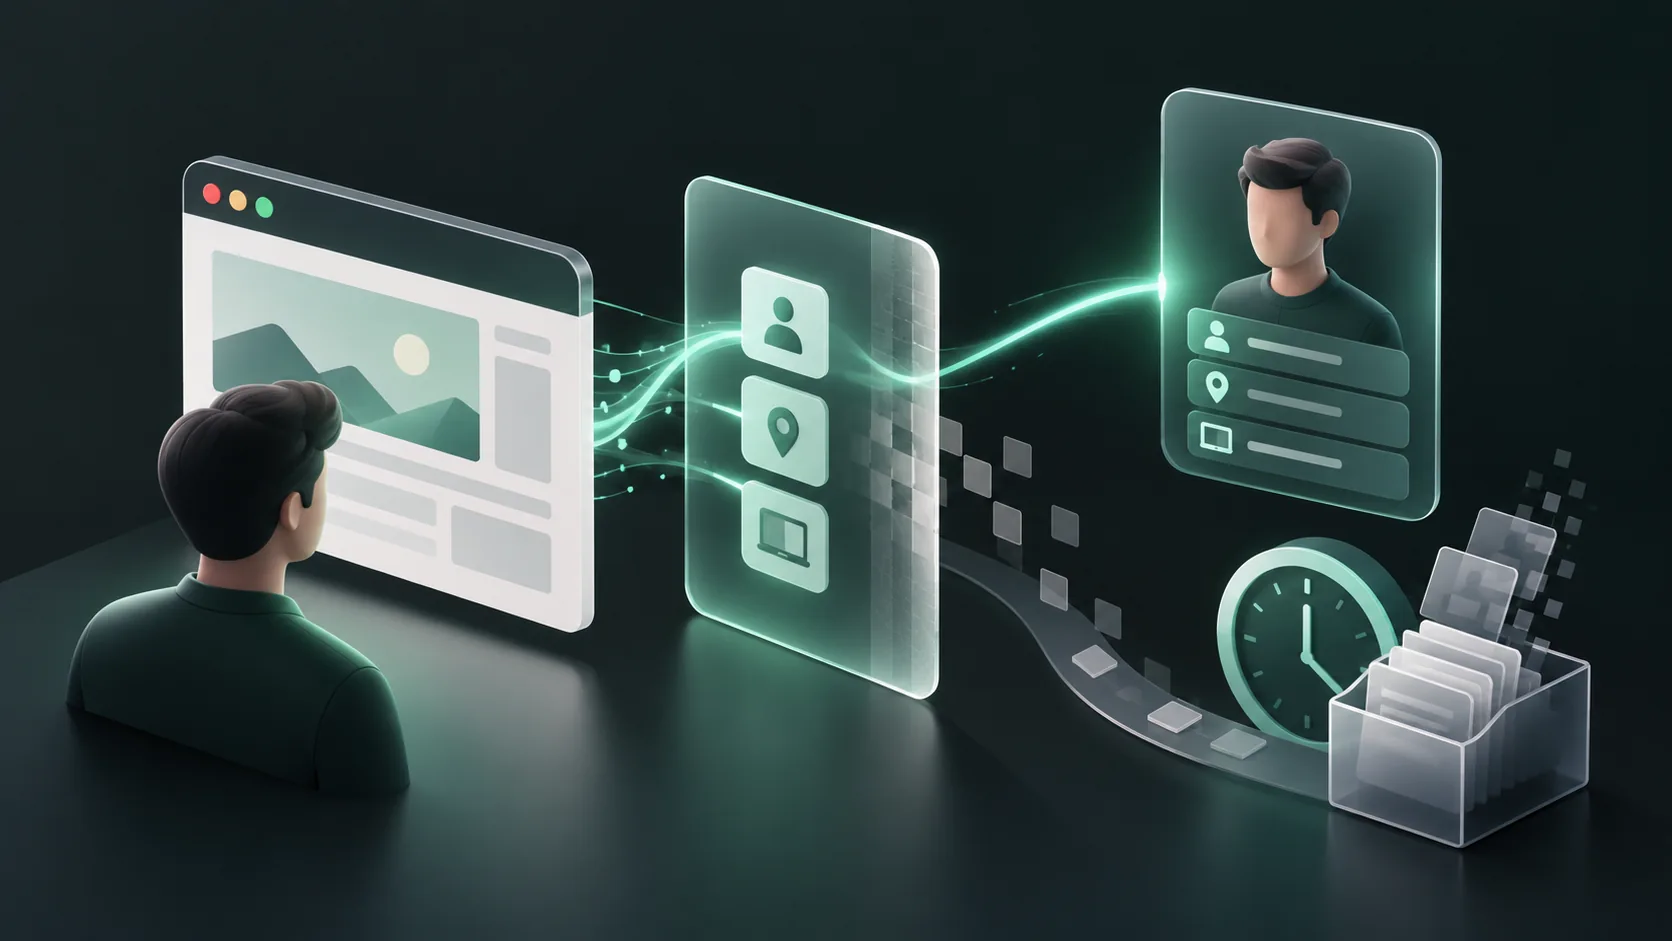
Cookieless visitor identification associates visits using evidence other than a stored browser cookie. It can help recognize a returning environment, investigate repeated account activity and preserve a product preference. It does not establish a person's legal identity, guarantee recognition after every change or remove the need to define collection, disclosure, retention and deletion policies.
Start by naming the object you want to recognize. A session, browser installation, physical device, signed-in account and person are different objects. An identifier can be useful even when it is probabilistic or changes, provided the application understands that scope and keeps a correction path.
What can a cookieless identifier establish?
An identifier establishes an association under a provider's model and available observations. Treat it as evidence for a stated workflow. The same browser may be used by two household members, while one person may use several browsers or devices. A change in identifier can mean a changed environment rather than a new customer.
The ShieldLabs identification documentation is a useful reference for the entities a provider exposes. Compare that contract with the identification product description. The contract should tell you what an event identifier refers to and how it differs from a persistent visitor or device identifier.
| Object | Useful question | Mistake to avoid |
|---|---|---|
| Session | Which interaction belongs to this visit? | Treating a session as a permanent identity |
| Browser or device association | Has this environment been observed before? | Equating an environment with a unique human |
| Account | Which authenticated user owns this action? | Trusting an account name supplied by the browser |
| Benefit claim | Has the eligible beneficiary received this offer? | Replacing the benefit ledger with an identifier |
For example, a trial policy may restrict repeated grants. The relevant decision is whether this claim qualifies, using account history and device evidence. Recognition is one input; the application still needs an idempotent grant record. Our free-trial guide explains that distinction.
How should collection be minimized?
Collect evidence for an explicit action and avoid attaching unrelated personal details to every event. Write down which application fields are needed, what they mean and who can retrieve them. A stable pseudonymous account reference may support account associations without sending the person's display name or complete customer record.
Pseudonymous does not mean anonymous. A durable identifier joined to account history can be sensitive even when it contains no readable name. Evaluate the actual collection and relationships described in ShieldLabs' privacy documentation, rather than interpreting a marketing phrase as a complete data-handling assessment.
A practical design review records the purpose of collection, the event that starts it, the fields sent, the parties receiving them, the retention window and the deletion route. Separate fraud prevention from personalization so that a change in one purpose does not silently expand the other. Use appropriate reviewers for the jurisdictions and user populations involved.
Where do consent and notice fit into the design?
The implementation must support the policy the business adopts. Identify where notices are displayed, whether any collection depends on a consent choice, how that choice reaches the application and what happens if a user declines. Installing a different technical identifier does not resolve those questions automatically.
Review the provider's tracking policy alongside its privacy policy. These are statements about the provider's service, not a declaration that every customer's deployment has the same purpose or legal basis. Record the version reviewed and the customer-side configuration that matters.
As an engineering example, do not start optional personalization collection before the application's choice is known, then attempt to repair the record afterward. Conversely, do not describe every fraud check as optional analytics merely because both appear in one dashboard. Keep the purposes and controls understandable to the people implementing and reviewing them.
What changes when a visitor returns?
A returning observation can support an application preference or investigation; it should not silently authorize an account action. Reuse low-risk preferences under an appropriate policy, then ask for separate authorization before changing credentials, delivering value or exposing private records.
Our new-versus-returning visitor guide explains why a returning device is not a returning customer count. The device-versus-wallet comparison adds another boundary: a wallet signature proves control of a key, while a device association describes observed context. Neither alone proves benefit eligibility.
For a shared library computer, keep an unsigned visitor preference separate from the signed-in account. A second customer should not inherit the first customer's private cart, entitlement or account history. In a fraud review, retain the uncertainty instead of turning the shared device into an automatic accusation.
How should retention and deletion be tested?
Use a small, documented set of test accounts to follow an observation through collection, retrieval, account association and deletion. Check the dashboard, API and any copied analytics or warehouse data. A deletion process is incomplete if the application removes one profile but keeps a second copy that still drives decisions.
Choose retention by the decision that needs the evidence. A short-lived signup check and a disputed transaction investigation can have different operational windows. Keep the configured window, access roles and export destinations in the review record, and revisit them when the workflow changes.
A useful test report states what was deleted, what was retained for a stated reason, which downstream systems were checked and what could not be verified. It does not claim perfect anonymity or universal compliance from a successful API response. The provider comparison guide describes how to request that evidence during a pilot.
Frequently asked questions
Does cookieless mean anonymous?
No. A persistent identifier and its account associations may still describe a recognizable environment or user relationship. Evaluate the data collected, its purpose, access and retention rather than relying on the absence of a cookie.
Can a device identifier replace account authentication?
No. It can inform a risk decision, but authentication and authorization must still establish who may perform the requested action. A familiar environment does not independently prove current account ownership.
Should every returning visitor receive the previous user's preferences?
Only under an appropriate product and privacy policy. Shared environments require particular care, and a visitor-level preference must not expose another account's private information or entitlement.
What should a retention test record?
Record the identifiers, systems, configured retention, deletion requests and downstream copies examined. State any unverified boundary rather than describing a partial deletion as a complete result.
Sources and editorial scope
This is an engineering review framework, supported by the linked documentation. ShieldLabs is part of the project portfolio. Provider policies and examples are sources to inspect, not independent proof of compliance or identification performance.
Further sources for cookieless visitor identification
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs documentation: Browser support | Check this operational reference for the current contract, limits, supported behavior or correction path. |
| Cookie Deprecation: What Changes for Measurement and Fraud Detection | Background on What Is the Real Cookie Deprecation Impact on the Browser Landscape Today?. Verify implementation details in the primary references. |
| Cookieless device identification: how to recognize a returning device without cookies | Background on What is cookieless device identification?. Verify implementation details in the primary references. |
| Web Device Binding: Coarse Fingerprints Link Visits for Fraud Teams | Background on What device binding means and where it fits in a fraud stack. Verify implementation details in the primary references. |
| How to Evaluate Device Fingerprinting Accuracy on Real Traffic | Background on What does fingerprinting accuracy actually measure?. Verify implementation details in the primary references. |
| Device Fingerprinting for Fraud: GDPR and UK PECR Considerations | Background on How device fingerprinting works for fraud detection. Verify implementation details in the primary references. |
| Developers: 5 Steps to Reliable Persistent Device IDs | Background on What Is a Persistent Device ID, and When Should You Use One?. Verify implementation details in the primary references. |
| Privacy Preserving Identification: 897 Risk Flags for Business Teams | Background on How Privacy-Preserving Visitor Identification Works. Verify implementation details in the primary references. |
| What was Google's Privacy Sandbox, and why did it end in 2025? | Background on What was the Privacy Sandbox?. Verify implementation details in the primary references. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


