
Free Trial Abuse Prevention: SaaS, AI Credits and Crypto APIs
Free Trial Abuse Prevention: SaaS, AI Credits and Crypto APIs. Compare evidence, practical controls and limitations, with related implementation sources.
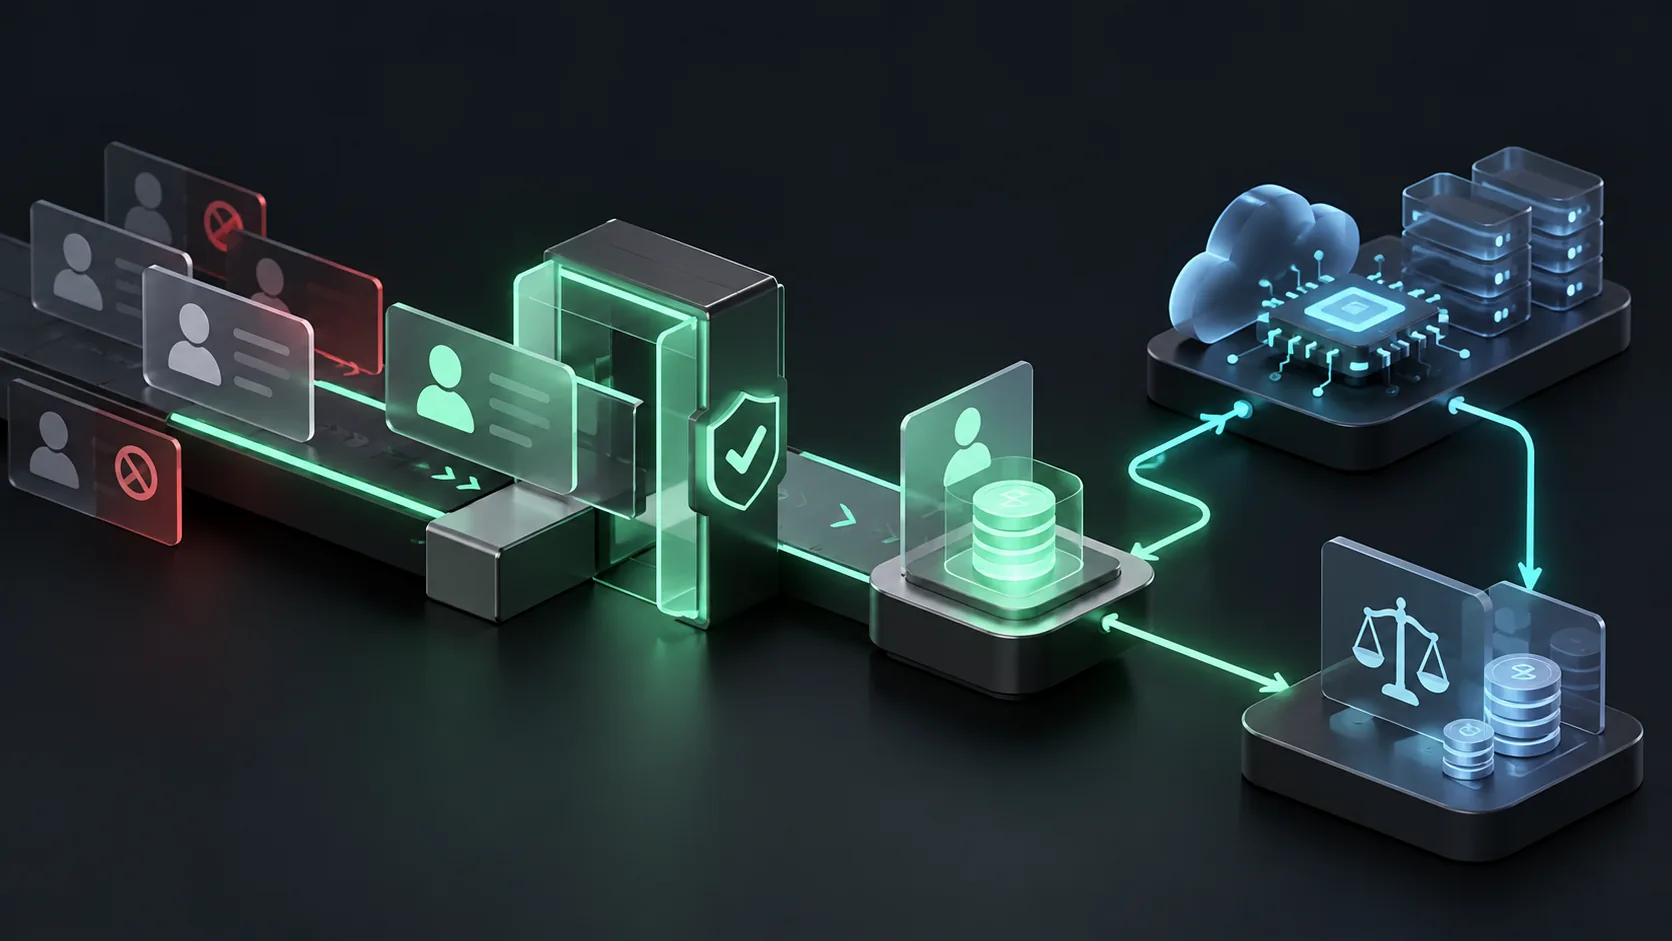
Free trial abuse prevention controls repeated eligibility for free access or credits. Useful evidence connects the account, benefit grant, returning environment and later usage. Enforce the grant on the server before expensive consumption, while retaining a legitimate evaluation path for shared devices and returning prospects. Rate limits and eligibility checks address different failures.
This article breaks down how the pattern works in Web3, why free infrastructure is such a soft target, how it overlaps with sybil attacks and airdrop farming, and the layered defenses that actually raise the cost of abuse.
What Is Free Trial Abuse?
Free trial abuse is the deliberate, repeated exploitation of a free tier or trial offer by a single actor posing as many new users. Each fresh signup looks legitimate in isolation, but together they let one operator extract resources priced for genuine, one-per-person usage without ever converting to a paid plan.
The mechanics are simple and cheap. An abuser cycles through disposable email addresses, spins up fresh wallets, and hides behind VPNs, proxies, or datacenter IPs so every "new" account appears unrelated. This is multi-accounting fraud at its core: one human, many masks. Naive limits based on a single email or IP address rarely stop it, because those identifiers are the easiest things to rotate.
How Free Trial Abuse Hits Crypto Infrastructure: RPC, APIs, Faucets, and Trial Credits
Free trial abuse hits crypto infrastructure wherever a resource is metered per user but handed out for free. Sybils script fresh wallets and accounts to claim RPC request quotas, hosted API keys, testnet faucet drips, and promotional trial credits far past intended limits, shifting the cost of their activity onto the provider and onto real users.
RPC free tier abuse is the most direct hit: node providers offer a monthly request allowance per account, so an operator registers dozens of accounts to run indexing bots or farming scripts at zero cost. Testnet faucet abuse is similar, where automated wallets drain the tokens meant to help real developers test contracts. Trial credits for analytics dashboards, indexing APIs, and dev tooling get harvested the same way. The result is degraded service for legitimate builders and a support bill the provider never planned for.
Why Sybils Target Free Tiers and Testnet Faucets
Sybils target free tiers and testnet faucets because these resources are cheap to attack and directly convertible into value. Faucet tokens fuel testnet activity that later qualifies wallets for airdrops, free RPC calls power farming bots at no cost, and each disposable identity resets the meter, turning a per-user allowance into an effectively unlimited supply.
The economics are proven at scale. In May 2022, Optimism applied extra sybil filtering to its first OP airdrop that excluded 17,000 addresses and recovered 14 million OP, then redistributed those tokens to legitimate recipients. Source: https://github.com/ethereum-optimism/community-hub/blob/main/pages/op-token/airdrops/airdrop-1.mdx — the wallets behind operations like these are routinely warmed up on free faucets and free RPC endpoints, which makes free-tier abuse the on-ramp for larger sybil campaigns. A year later the same pattern surfaced at greater scale: an analysis of Arbitrum's 2023 ARB airdrop estimated that sybil clusters captured roughly 21.8% of the distribution, about 253 million ARB, despite anti-sybil filtering. Source: https://crypto.news/arbitrum-airdrop-marred-by-sybil-attacks/
Free Trial Abuse vs. Sybil Attacks vs. Airdrop Farming
Free trial abuse, sybil attacks, and airdrop farming overlap but are not identical. Free trial abuse is the outcome (unlimited free resources), a sybil attack is the technique (one operator running many fake identities), and airdrop farming is a common motive (qualifying many wallets for a token distribution). In crypto, the three usually appear together as one operation.
| Concept | What it is | Primary goal | Core method | Best defense |
|---|---|---|---|---|
| Free trial abuse | Repeated free-tier consumption | Unlimited free resources | Disposable identities, multi-accounting | Identity and usage correlation |
| Sybil attack | One actor, many fake identities | Fake scale or influence | Scripted wallets, proxies, VPNs | Sybil resistance, reputation scoring |
| Airdrop farming | Many wallets farmed for rewards | Maximize token allocation | Wallet warming, faucet and testnet activity | On-chain reputation, proof of humanity |
Warning Signs of Free Trial Abuse
The clearest warning sign of free trial abuse is a spike in new accounts that share hidden traits while looking superficially distinct. Watch for bursts of signups from datacenter IPs, freshly created wallets with no real history, disposable email domains, and usage that skips onboarding and jumps straight to high-value, resource-heavy calls.
Look for these correlated red flags:
- Many new wallets or accounts created inside tight time windows
- Traffic concentrated on VPN, proxy, or datacenter IP ranges
- Disposable or pattern-generated email addresses
- Wallets with zero prior on-chain history claiming faucets or credits
- Identical device fingerprints across "different" users
- Instant, maximal resource use with no exploratory behavior
Any one of these can be innocent. Several appearing together across a cohort of accounts is the signature of a single operator.
How to Detect and Prevent Free Trial Abuse
You detect and prevent free trial abuse by correlating signals that a single operator cannot easily fake across all of their fake accounts. No single check is enough; the goal is to raise the cost of each new identity until abuse stops paying for itself. Combine device, network, behavioral, and, in crypto, on-chain reputation signals.
Traditional web platforms have refined this over a decade, and teams running free RPC endpoints, faucets, and API tiers increasingly adapt prevention playbooks built specifically for free-tier and trial abuse to Web3 conditions. The practical controls are consistent: rate limiting per correlated identity rather than per raw email or IP, disposable-email and datacenter-IP filtering, device fingerprinting to catch repeat visitors, and a proof-of-humanity or reputation gate before a wallet can claim scarce free resources. Developers who ship these layers together can reduce repeated claims, but must measure legitimate-user challenges and missed abuse in their own traffic.
Device Signals vs. On-Chain Reputation: A Layered Defense
Device signals and on-chain reputation defend different flanks, so a strong layered defense uses both. Device and network signals (fingerprint, disposable email, VPN, proxy, datacenter IP) catch abuse at the web layer before a request lands. On-chain reputation judges the wallet itself, catching sybils whose browser looks clean but whose address has no genuine history.
Each layer covers the other's blind spot. Web-layer signals can be defeated by anti-detect browsers and residential proxies, which make a scripted farm look like thousands of distinct humans. On-chain history is far harder to fake, because a credible track record across many protocols and chains costs real capital and real time. A sybil can rotate IPs in seconds, but it cannot instantly manufacture years of authentic activity for a thousand wallets.
Proof-of-Human ID and Reputation Scoring as a Sybil-Resistance Layer
Proof-of-human identity and reputation scoring add a sybil-resistance layer that device checks alone cannot provide: they price identity in real, verifiable on-chain activity. A wallet that has genuinely used many protocols across many chains is costly to fabricate at scale, so scoring that behavior lets protocols separate real users from disposable sybil wallets.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
Is Free Trial Abuse Illegal?
Contract enforcement and criminal liability are different questions. The outcome depends on the conduct, applicable terms and jurisdiction; a terms violation should not automatically be described as a crime. Stolen payment details or identity misuse require separate assessment. Obtain qualified jurisdiction-specific advice for a legal conclusion.
The everyday case is different from abuse. If you sign up for one trial, add a card, and forget to cancel, you can be charged when the trial converts to a paid plan; that is ordinary billing, not fraud. Trial spam, by contrast, means continuously creating new accounts to dodge limits, and while it rarely leads to prosecution, it reliably leads to bans and forfeited rewards once a provider correlates the accounts. In crypto, sybil farming of airdrops sits in a grayer zone, where projects routinely disqualify wallets and reclaim tokens rather than pursue courts.
Free-trial abuse prevention for SaaS and AI compute
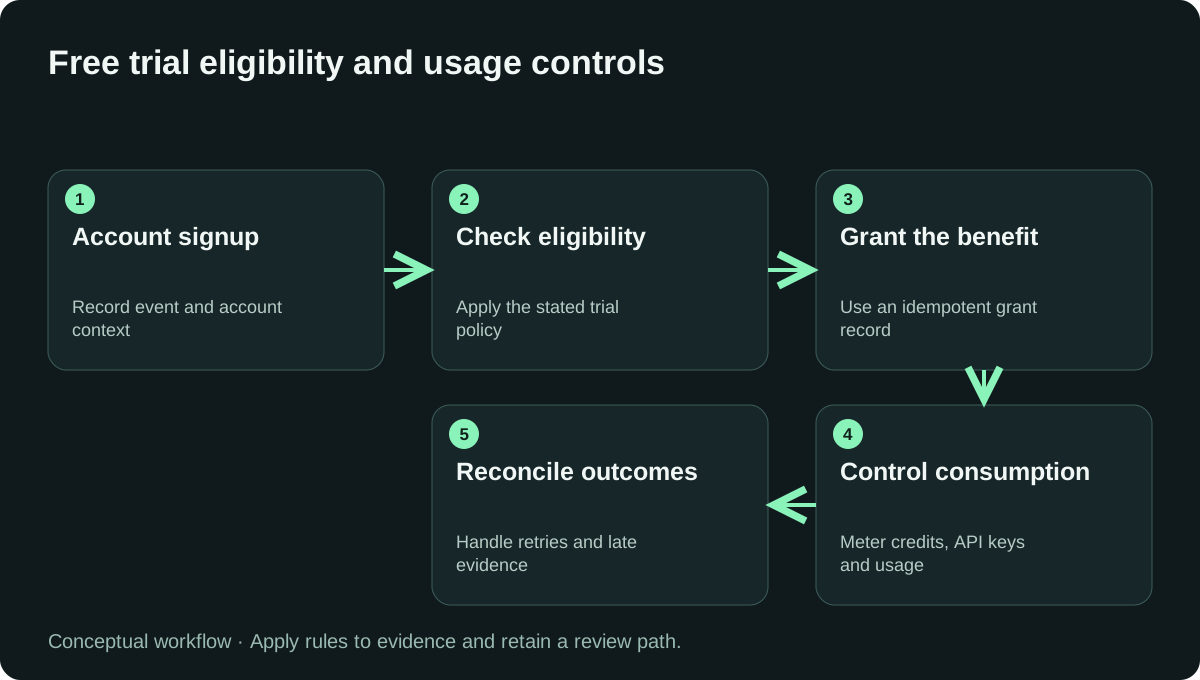
Free-trial abuse prevention starts with the benefit grant. An AI product should connect the trial entitlement to the account and relevant returning-device evidence before expensive inference begins. Per-key rate limits bound consumption through one key; they do not establish that a newly created account deserves another grant.
Maintain an idempotent server-side entitlement ledger. Record the grant, subsequent usage and any review outcome. Shared devices and returning prospects need an evaluation path, so do not treat every repeat visitor as an abuser. The protected unit is an eligible grant, not simply a successful signup.
For implementation context, see free-trial abuse controls and AI trial-abuse guide. Related editorial sources include Medium analysis of the free-trial grant as the risk unit, Medium guide to preventing trial abuse, DEV comparison of trial abuse, API-key abuse and rate limits. Read next: best fraud detection apis developers 2026, new account fraud fresh wallet risk.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best Free Trial Abuse Prevention Tools in 2026.
Frequently Asked Questions
What is free trial abuse in crypto? Free trial abuse in crypto is when sybils create many wallets or accounts with fake or disposable identities to repeatedly drain free-tier resources, such as RPC and API request quotas, testnet faucet tokens, and trial credits. The goal is unlimited free usage, which inflates provider costs and pollutes on-chain activity data.
How do sybils abuse testnet faucets and RPC free tiers? Sybils script hundreds of fresh wallets and route them through proxies or VPNs to claim testnet faucet drips and free RPC or API keys past the intended per-user limits. Each identity looks new, so naive email- or IP-based caps fail, letting one operator consume resources meant for thousands of real users.
Is free trial abuse illegal? Free trial abuse is usually not a criminal offense, but it almost always violates a service's terms of use, which can trigger account bans, credit clawbacks, and civil liability. When it involves stolen cards, synthetic identities, or fraud against token airdrops, it can cross into legally actionable territory depending on jurisdiction.
How do you detect free trial abuse? Detection combines device signals (fingerprint, browser and hardware traits), network signals (proxy, VPN, datacenter IP), behavioral signals (skipped onboarding, instant high-value usage), and, in crypto, on-chain reputation that scores a wallet's real history. Correlated signals expose many accounts run by one operator even when emails and IPs differ.
Can on-chain reputation prevent free trial abuse? On-chain reputation helps prevent free trial abuse by scoring a wallet's genuine multichain activity, so fresh, empty sybil wallets score low and can be rate-limited or denied free resources. Paired with a proof-of-human identity check, it raises the cost of spinning up disposable accounts without blocking legitimate users.
What is the difference between free trial abuse and a sybil attack? Free trial abuse is the goal (extracting free resources), while a sybil attack is the method (one operator running many fake identities). In crypto, most free-tier and faucet abuse is executed as a sybil attack, so sybil-resistance techniques like reputation scoring and proof-of-human checks are the core defense.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] free-trial abuse controls — vendor product scope.
[2] AI trial-abuse guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for free trial abuse prevention
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs documentation: Free-trial abuse | Relate this scenario to the application action, qualification rule and later outcome record. |
| The 8 best free-trial abuse prevention tools in 2026 | Background on What is free-trial abuse prevention?. Verify implementation details in the primary references. |
| Detect Free Trial Abuse with 300+ Signals for SaaS Teams | Background on What Is Free Trial Abuse and Why Does It Matter for SaaS?. Verify implementation details in the primary references. |
| Free-trial abuse vs API-key abuse vs rate limiting: which layer stops what | Background on The three problems people blame for one bill. Verify implementation details in the primary references. |
| How to prevent free-trial abuse without losing real customers | Background on What is free-trial abuse?. Verify implementation details in the primary references. |
| Trial farming and credit farming on AI products: how one operator drains your free credits | Background on What is trial farming and credit farming (not the gaming kind)?. Verify implementation details in the primary references. |
| Fraud prevention for AI products. | Read the provider-stated product or use-case scope; verify the selected integration before applying a policy. |
| Fraud prevention for SaaS. | Read the provider-stated product or use-case scope; verify the selected integration before applying a policy. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


