
VPN Detection Tools: IP Evidence, Location and False Positives
VPN Detection Tools: IP Evidence, Location and False Positives. Compare evidence, practical controls and limitations, with related implementation sources.
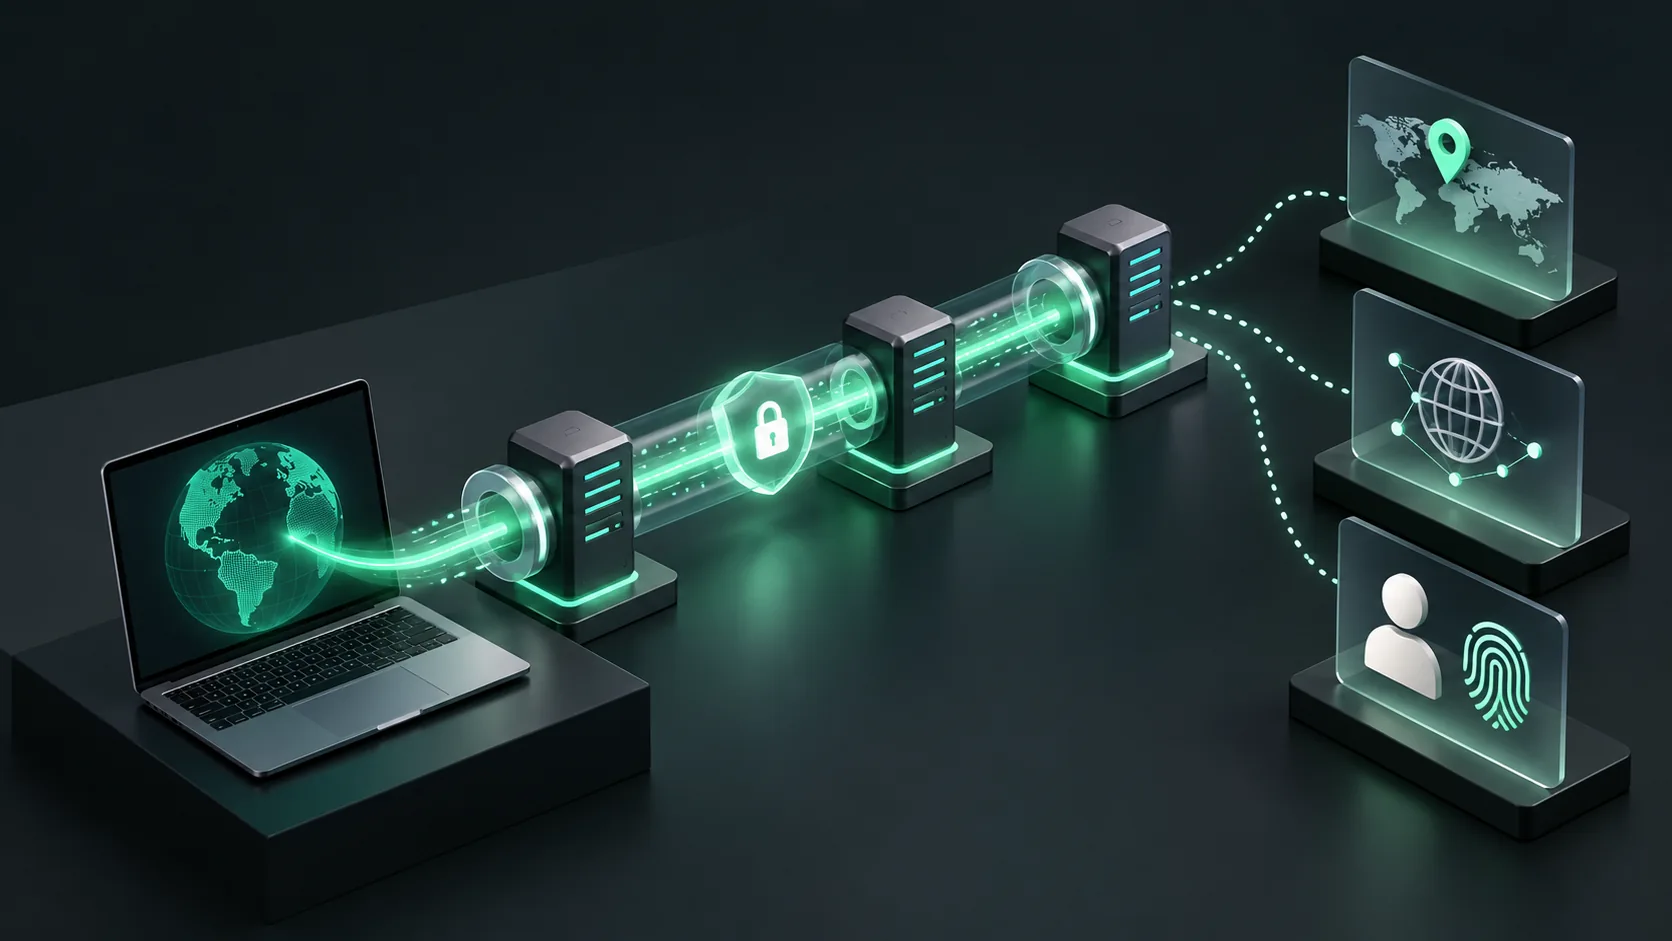
VPN detection tools evaluate connection evidence associated with tunneled or relayed traffic. Providers differ in the categories, freshness and context they return. A VPN flag is not proof of fraud or verified physical location; apply an action-specific policy that considers legitimate privacy users, shared networks and supporting account evidence.
For Web3 teams, that question is not academic. When one operator can make a single wallet look like a thousand users behind rotating IPs, quest rewards and airdrop allocations drain toward farmers instead of real participants. This guide explains how VPN detection works, where it breaks, and why durable sybil resistance needs an on-chain layer on top of the network layer.
What Is VPN Detection?
VPN detection is the practice of determining whether an incoming connection is masked by a VPN, proxy, or Tor tunnel rather than a genuine consumer ISP. Detection engines answer one question — is this IP hiding the user's real network and location — by scoring the connection against reputation data and live technical signals.
The output is usually a probability or risk score, not a hard yes-or-no verdict. A connection from a known cloud datacenter range scores high; a residential mobile IP scores low. Protocols use that score to gate rewards, throttle suspicious sessions, or flag wallets for manual review.
How VPN Detection Works: The Core Signals
VPN detection works by fusing several independent signals into one risk score. The foundation is IP reputation — checking whether an address belongs to a datacenter ASN (Autonomous System Number) or a published VPN exit-node list — layered with live checks: timezone-to-IP geolocation mismatch, WebRTC and DNS leaks, open proxy ports, and TCP/TLS network fingerprinting.
No single signal is conclusive. Each one produces false positives, so engines weight them together rather than trusting any one check. The core inputs:
- ASN and datacenter lookup — most commercial VPNs host exit nodes in cloud datacenters; consumer traffic almost never originates from those ranges.
- IP geolocation mismatch — the browser reports one timezone or language while the IP address geolocates to a different country.
- WebRTC and DNS leaks — misconfigured tunnels expose the user's real IP through browser APIs or DNS resolvers.
- Network fingerprinting — MTU size, TCP timestamps, and TLS handshakes can betray a tunnel even when the IP looks clean.
Why VPNs and Geo-Spoofing Threaten Crypto Quests and Airdrops
VPNs and geo-spoofing threaten crypto incentives because they let one person appear as many independent users in many places. Airdrop and quest budgets assume roughly one human per allocation; a farmer running dozens of wallets behind fresh IPs collects a disproportionate share, diluting rewards for genuine community members and distorting protocol growth metrics.
The scale is documented. Ahead of its June 2024 ZRO token distribution, LayerZero published a preliminary list of 803,093 wallet addresses flagged as potential sybils, refined down from more than two million it had initially flagged; addresses that self-reported were set to receive 15% of their allocation. Source: https://crypto.news/layerzero-spots-800k-sybil-addresses-airdrop-scheme/ (crypto.news, May 2024).
How Farmers Use VPNs to Bypass Region Gates
Farmers use VPNs and proxies to defeat region gates by selecting an exit node in a permitted country, making a blocked jurisdiction look eligible. Combined with anti-detect browsers that spoof device fingerprints, one operator can present each wallet as a distinct user in a distinct location, passing naive geofencing checks one session at a time.
This matters beyond fairness. Projects that gate token sales or airdrops to steer clear of sanctioned regions rely on location accuracy, and a spoofed IP can route a user past an OFAC-driven geofence. Region gating built only on raw IP geolocation is therefore easy to circumvent and should never be the sole control.
VPN vs. Proxy, Residential Proxy, and Tor Detection: A Comparison
VPNs, proxies, residential proxies, and Tor all anonymize traffic, but they differ in how they route it and how hard they are to detect. Datacenter VPNs and public proxies are the easiest to catch because their IPs sit in flagged ranges; residential and mobile proxies are the hardest because they borrow real consumer IPs that pass reputation checks.
| Tunnel type | How it routes traffic | Typical IP source | Detection difficulty |
|---|---|---|---|
| Datacenter VPN | Encrypted tunnel to a hosted exit node | Cloud datacenter ASN | Low |
| Public / HTTP proxy | Relays requests, often unencrypted | Datacenter or flagged ranges | Low |
| Residential proxy | Routes through real consumer devices | ISP-assigned home IPs | High |
| Mobile proxy | Routes through cellular carrier IPs | Carrier-grade NAT ranges | Very high |
| Tor | Multi-hop onion routing | Public exit-node list | Low (list-based) |
The Limits of IP-Based VPN Detection
IP-based VPN detection has a hard ceiling: it can only judge the connection, not the person behind it. Residential and mobile proxies route through legitimate consumer IPs that reputation databases rate as clean, and anti-detect browsers reset device fingerprints per session, so a funded farmer can push detection accuracy well below what datacenter checks alone suggest.
That gap is why teams treat detection scores as probabilistic and benchmark vendors carefully; a closer look at how detection engines weigh these network signals in practice shows how much the same IP can score differently across providers. IP signals stay necessary, but on their own they cannot separate one well-resourced farm from a thousand real users.
Beyond the IP: On-Chain Reputation as a Sybil-Resistance Layer
On-chain reputation adds the layer that IP checks miss: it scores a wallet's history instead of the connection's network. Because a farmer has to fund, age, and diversify every wallet to fake credible activity, evaluating behavior across chains raises the cost of a sybil attack far beyond what rotating IPs can defeat.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
An on-chain attestation can make a recorded claim available to a receiving application. Acceptance, eligibility thresholds and ecosystem scope still depend on that application. A published score is not an automatic guarantee of transparent computation, universal portability or unique-person identity.
How Protocols Should Combine Network and On-Chain Signals
Protocols get the strongest sybil resistance by layering two systems: network-level VPN detection to flag the connection, and on-chain reputation to judge the wallet. The IP layer catches the tunnel in real time; the reputation layer catches the farm behind it even when the IP looks perfectly residential.
A practical stack looks like this:
- Screen the connection — run VPN and proxy detection at session start to produce a network-risk score.
- Score the wallet — check on-chain reputation and humanness before granting any reward.
- Gate on the combination — require both a low network-risk score and a credible reputation score to claim, so passing one check is not enough.
VPN Detection Tools and APIs
VPN detection tools fall into two groups: IP-intelligence APIs that classify addresses, and device-intelligence services that fingerprint the browser. Most teams query one at session start through a VPN detection API and read back a risk score. Common options include IPQualityScore and MaxMind for IP reputation and geolocation, and Fingerprint for device-level signals.
For Web3, these network tools pair with on-chain reputation rather than replace it. IP APIs answer "is this connection masked," while reputation scoring answers "is this wallet a real, active user." A complete anti-sybil pipeline reads both and decides on the combination.
Is Using a VPN Illegal?
Using a VPN is legal in most countries, including the United States, and is a mainstream privacy and security tool.
No U.S. state bans VPNs. A handful of countries, such as China, Russia, and Iran, restrict or heavily regulate them, but that is the exception rather than the rule. The legal risk is rarely the VPN itself; it is using one to bypass terms of service or region gates, for example claiming a geofenced airdrop from a blocked or sanctioned jurisdiction.
VPN detection and location policy beyond crypto
VPN detection can support account and network review in SaaS, ecommerce and gaming. A VPN is a routing observation, not proof of fraud or physical location. Travelers, employees and privacy-conscious customers may use relayed connections legitimately.
Evaluate the sensitive action rather than block every flagged visitor. Combine network findings with account history and an appropriate challenge or review path. Where a product needs specialist location verification, assess that requirement separately from a general IP lookup.
For implementation context, see VPN and proxy controls and VPN detection guide. Related editorial sources include Medium explanation of VPN false-positive policy. Read next: anonymity check ip risk score, best gaming fraud prevention tools 2026.
What should a reproducible review preserve?
- The protected action and applicable eligibility rule.
- The original observation, its source and timestamp.
- Missing evidence and unresolved identity relationships.
- The decision reason and any additional verification.
- Appeals, reversals and later confirmed outcomes.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best VPN and Proxy Detection Tools in 2026.
Frequently Asked Questions
Is it possible to detect a VPN?
Yes. VPN detection identifies masked connections with high accuracy by cross-referencing an IP against databases of known datacenter ranges and VPN exit nodes, then confirming with live signals like timezone-to-IP geolocation mismatches and WebRTC leaks. No single method is perfect, so detection engines combine several signals into one risk score rather than relying on a single check.
How do crypto projects detect VPNs and geo-spoofing during airdrops?
Crypto projects layer two systems. Network-level VPN detection flags the connection using datacenter IPs, proxy exit nodes, and geolocation mismatches, while on-chain analysis inspects wallet behavior for sybil patterns such as common funding sources, identical transaction timing, and low activity diversity. IP signals catch the tunnel; on-chain reputation catches the farm behind it.
Can VPN detection be bypassed?
Partially. Residential and mobile proxies route traffic through real consumer IPs, and anti-detect browsers spoof device fingerprints, both of which lower IP-based detection accuracy. This is why protocols that need durable sybil resistance pair VPN detection with on-chain reputation scoring, which evaluates wallet history rather than the connection's IP address.
Is using a VPN illegal?
Using a VPN is legal in most countries, including the United States, and is common for privacy and security. It becomes a policy problem when used to bypass region gates or terms-of-service restrictions, for example accessing a geofenced airdrop or token sale from a sanctioned or blocked jurisdiction.
What is the difference between VPN detection and sybil detection?
VPN detection answers whether a single connection is anonymized at the network layer. Sybil detection answers whether many accounts or wallets are controlled by one entity. A farmer can pass one check and fail the other, so quest and airdrop platforms need both to reliably filter bots and reward genuine users.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] VPN and proxy controls — vendor product scope.
[2] VPN detection guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for vpn proxy detection tools
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs documentation: Regional pricing | Relate this scenario to the application action, qualification rule and later outcome record. |
| How to detect geolocation spoofing and prevent fraud | Background on TL;DR. Verify implementation details in the primary references. |
| Time Zone Fraud: 6 Signals Security Teams Can Verify in Logs | Background on Where does time zone data come from, and how is it manipulated?. Verify implementation details in the primary references. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


