
Proxy Detection API: VPN Signals, Trusted IPs and Integration
Proxy Detection API: VPN Signals, Trusted IPs and Integration. Compare evidence, practical controls and limitations, with related implementation sources.
A proxy detection API supplies provider-defined observations about an IP address or connection, such as VPN, proxy, Tor or hosting indicators. A reliable integration uses a trustworthy source IP, checks the response contract and records unknowns. These observations enrich an account decision; they do not establish ownership, intent or unique-person eligibility.
What is a proxy and VPN detection API?
A proxy and VPN detection API is a web service that accepts an IP address and returns whether it belongs to a VPN, proxy, hosting provider, or Tor node, plus a risk score. Protocol and quest teams call it during signup or claim flows to flag anonymized connections before granting rewards.
The value is speed and coverage. Instead of maintaining IP blocklists yourself, you query a provider that already tracks millions of flagged ranges and updates them continuously.
The terms VPN detection API and proxy detection API usually describe the same product, since providers flag both connection types from a single endpoint and return them as separate fields.
How does proxy and VPN detection actually work?
Detection works by matching an IP against databases of known VPN and proxy ranges, then analyzing its Autonomous System Number (ASN), data center origin, open ports, latency, and connection behavior. The API fuses these signals into flags and a numeric risk score, usually returned in well under a second.
Under the hood, providers combine several methods:
- Blocklist matching — the IP is compared to curated lists of commercial VPN and proxy endpoints.
- ASN analysis — an ASN identifies the network that owns the IP; ranges owned by hosting companies rather than consumer ISPs signal automation.
- Active probing — some services open test connections to fingerprint proxy ports.
- WebRTC signals — a client-side check can surface a WebRTC leak, where the browser exposes a real IP behind a VPN.
To check if an IP is a VPN or proxy manually, you would replicate this lookup by hand; an API does it at scale, on every request.
What signals does the API return? VPN, proxy, residential proxy, Tor, and data center flags
Most APIs return a set of boolean flags plus a risk score. The flags describe how the connection is anonymized, while the score expresses overall confidence that the traffic is high-risk. Reading them together matters more than trusting any single flag.
Common return fields:
- VPN — the IP belongs to a commercial virtual private network.
- Proxy — traffic is relayed through an intermediary, including open or SOCKS proxies.
- Residential proxy — a proxy routed through a real consumer device, the hardest type to detect.
- Tor exit node — the connection leaves the Tor network through a known exit relay.
- Data center IP — the address is hosted by a cloud provider, not a home ISP.
- Risk score — typically 0-100, aggregating the above with reputation history.
An IP reputation API layer adds context such as prior abuse reports and geolocation consistency, which sharpens the score.
Where proxy and VPN detection fits in a Web3 anti-sybil stack
Proxy and VPN detection belongs at the edge of your pipeline, as the first cheap filter before heavier checks. It removes the most obvious automation — data center IPs and shared proxies — so downstream identity and reputation systems spend resources only on plausible users. It is necessary but not sufficient for anti-sybil detection for Web3.
The scale of the problem justifies the layer. Before distributing its ZRO token in June 2024, LayerZero published a preliminary list of 803,093 wallet addresses flagged as potential sybils, refined down from more than two million it had initially flagged.
Source: https://crypto.news/layerzero-spots-800k-sybil-addresses-airdrop-scheme/ (crypto.news, May 2024)
The pattern repeats across major drops. Analytics firm X-explore identified 148,595 Arbitrum airdrop addresses as sybil, and separately found that at least 4,000 sybil communities captured more than 253 million ARB — roughly 21.8% of the distribution.
Source: https://crypto.news/arbitrum-airdrop-marred-by-sybil-attacks/
Filtering anonymized IPs early raises the cost of running these farms. But sophisticated operators route each wallet through a separate residential or mobile IP, which is exactly where network detection alone stops working.
Network signals vs. wallet reputation: why on-chain teams need both layers
Network signals answer "how is this user connecting?" while wallet reputation answers "does this user have a genuine history?" IP detection catches cheap, shared infrastructure; wallet reputation catches fresh, disposable identities that connect from clean IPs. Coordinated sybil farming defeats either layer used alone, so on-chain teams combine them.
| Layer | Catches | Blind spot |
|---|---|---|
| Proxy and VPN detection (network) | Data center IPs, VPNs, Tor, cheap shared proxies | Residential proxies, one clean IP per wallet |
| Wallet reputation (on-chain) | Fresh wallets, no real history, funding clusters | Aged wallets farmed or bought over months |
The layers cover each other's gaps. A farmer can rent a residential IP for pennies, but building a wallet with genuine multichain activity over months is far more expensive to fake.
Comparing proxy and VPN detection APIs for on-chain teams
There is no single "best" proxy and VPN detection API; the right choice depends on which signals you need and your query volume. Evaluate providers on residential proxy detection, Tor exit node detection, latency, false-positive rate, geolocation accuracy, and pricing at your scale rather than on headline feature counts.
Widely used providers include IPQualityScore (IPQS), IPinfo, IP2Proxy, proxycheck.io, ipgeolocation.io, and vpnapi.io. Several offer free tiers with monthly limits that suit testing, while production-grade residential proxy detection generally sits behind paid plans.
Because feature coverage and pricing shift often, many teams cross-check editorial breakdowns of how the leading proxy and VPN detection APIs compare before committing to one provider.
Weigh these criteria first:
- Residential proxy detection — the decisive capability for anti-sybil work.
- Latency and uptime — you are calling this inside a live claim flow.
- False-positive rate — over-blocking legitimate privacy users costs real conversions.
The limits of IP intelligence: residential proxies and false positives
IP intelligence has two hard limits. Residential proxies route through real consumer devices, so they present clean home IPs that most APIs cannot distinguish from genuine users. At the same time, aggressive flagging produces false positives that penalize legitimate users who simply run a VPN for everyday privacy.
Residential proxy detection is probabilistic, not certain. Providers infer it from subtle timing and reputation cues, and determined farmers will pay for IPs that pass.
False positives are the mirror risk. Blocking every flagged IP outright rejects real participants, so treat the score as an input to a decision, not the decision itself. This is precisely why network data needs a second, identity-aware layer.
Combining IP detection with on-chain reputation scoring
The strongest approach runs the IP check at the edge, then queries an on-chain reputation layer for the connecting wallet. A flagged IP raises suspicion, but a wallet with deep, genuine history can still pass, while a fresh wallet on a data center IP is escalated or blocked. The two scores together are much harder to game.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
An on-chain attestation can make a recorded claim available to a receiving application. Acceptance, eligibility thresholds and ecosystem scope still depend on that application. A published score is not an automatic guarantee of transparent computation, universal portability or unique-person identity.
A practical rule: let network detection decide how much scrutiny a connection gets, and let wallet reputation decide who actually qualifies.
Implementation checklist: adding detection to your sybil-filtering pipeline
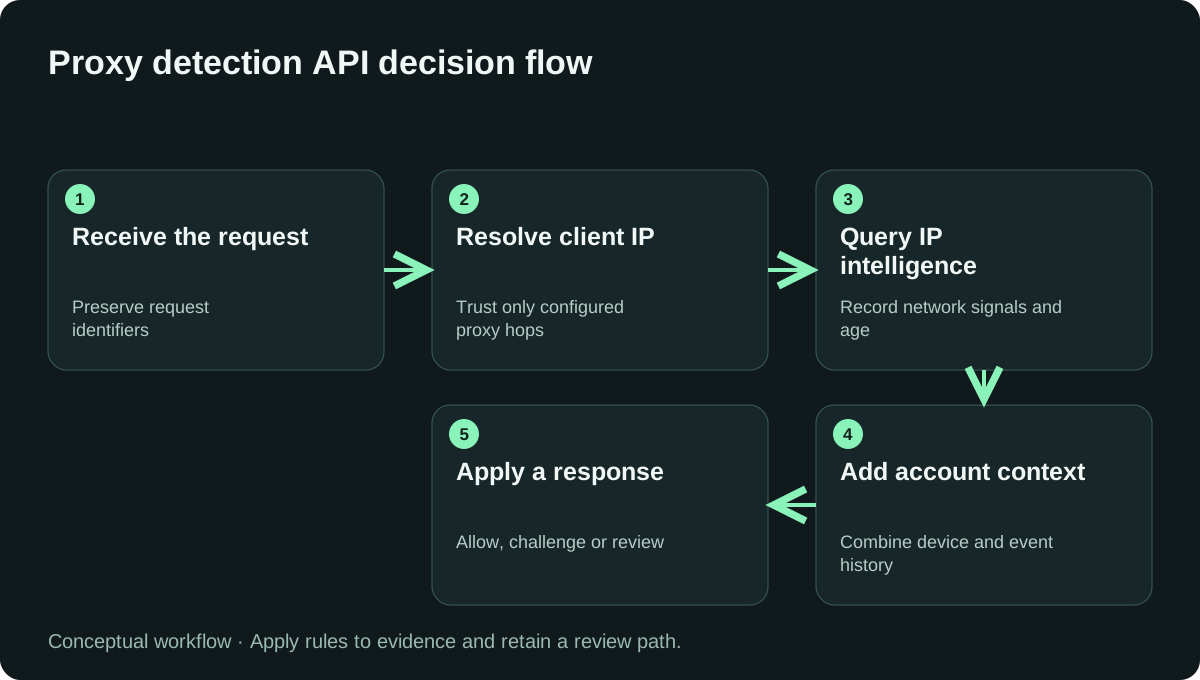
Add detection as an ordered pipeline, with the cheapest and fastest checks first. Call the proxy and VPN detection API at the network edge, apply a risk threshold, then pass borderline and passing users to wallet-reputation and identity checks. Log every decision so you can tune thresholds against real outcomes rather than guesses.
- Call the IP check on signup and on claim. Sybils often switch IPs between the two events.
- Set a risk threshold, not a hard block. Route high scores to extra verification.
- Query wallet reputation for every connecting address. Use MRS-style scoring plus a proof-of-human signal.
- Combine the two into one decision. Weight genuine on-chain history above a single IP flag.
- Snapshot eligibility at a fixed block. This prevents mid-flight gaming of the rules.
- Log and review each cycle. Track false positives and adjust thresholds over time.
Proxy detection API integration for any signup or payment flow
The proxy detection API comparison is a focused source for shortlisting services before testing their response contracts.
A proxy detection API integration needs a trustworthy source IP and a documented response contract. Behind a reverse proxy, accept forwarding headers only from infrastructure you control and trust. Otherwise a client may supply the address being assessed, making a valid lookup irrelevant to the real request.
Test IPv6, unknown classifications, timeouts and the provider's freshness. Preserve the observation at the protected action and avoid treating a missing response as a clean verdict. IP intelligence enriches a workflow; it does not establish account ownership or independently prove multi-accounting.
For implementation context, see proxy and VPN detection and proxy detection implementation guide. Related editorial sources include Medium proxy detection guide. Read next: anonymity check ip risk score, best fraud detection apis developers 2026.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best VPN and Proxy Detection Tools in 2026.
Frequently asked questions
How does a proxy and VPN detection API detect a VPN?
A proxy and VPN detection API compares an IP address against databases of known VPN, proxy, and hosting-provider ranges, then analyzes ASN ownership, data center origin, open ports, and connection behavior. It returns flags and a risk score in real time over an API call, so your app can act on the result before granting access.
Can proxy and VPN detection stop sybil attacks on its own?
No. IP intelligence filters anonymized and data center traffic, but determined sybil farmers rotate residential proxies and mobile IPs that look like real users. Stopping coordinated multi-account abuse requires layering network signals with device fingerprinting and on-chain wallet reputation that evaluates a wallet's genuine activity across chains.
Is there a free VPN or proxy detection API?
Yes. Several providers offer free tiers with monthly query limits, including proxycheck.io, vpnapi.io, and IPinfo, which suit testing or low-volume checks. High-volume production use, residential proxy detection, and guaranteed uptime generally require a paid plan.
Is using a VPN or proxy illegal?
Using a VPN or proxy is legal in most countries, including the United States, and many people use them for everyday privacy. Detection APIs do not judge legality; they flag anonymized traffic so teams can apply extra verification where anonymity correlates with fraud or sybil risk.
How do you combine IP detection with wallet reputation?
Run the IP check at the edge to score connection risk, then query an on-chain reputation layer for the connecting wallet. A wallet with genuine multichain history and a high humanness score can pass despite a flagged IP, while a fresh wallet on a data center IP is escalated or blocked.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] proxy and VPN detection — vendor product scope.
[2] proxy detection implementation guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for proxy detection api
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs network signals research archive | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| ShieldLabs network signals research archive — page 2 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


