
Payment Fraud Prevention: Checkout, Chargebacks and Crypto On-Ramps
Payment Fraud Prevention: Checkout, Chargebacks and Crypto On-Ramps. Compare evidence, practical controls and limitations, with related implementation sources.
Payment fraud prevention evaluates unauthorized or deceptive payment activity using transaction, account and fulfillment evidence. A merchant should connect provider results to the order before releasing value where possible. Crypto on-ramps add an important timing problem: a disputed card payment and an already-delivered on-chain transfer can have different reversal paths.
This article explains how payment fraud works at the fiat-to-crypto boundary, the main attack types, the warning signs, and the layered controls, including on-chain reputation, that catch a bad transaction before the crypto ever leaves.
What Is Payment Fraud?
Payment fraud is the illegal use of stolen or false payment information to obtain money, goods, or services without authorization. It covers card-not-present fraud, chargeback (friendly) fraud, account takeover, and card testing. At a crypto on-ramp the "good" is cryptocurrency, so one fraudulent charge becomes an irreversible on-chain transfer within minutes.
A common example: an attacker buys a batch of stolen card numbers on a darknet market, enters them at a fiat gateway, and converts each successful charge into Bitcoin or a stablecoin sent to a wallet they control.
Card fraud is a large and growing category. The Nilson Report put worldwide card fraud losses at $33.83 billion for 2023 and projected they would total $403.88 billion cumulatively over the next decade (Nilson Report, January 2025). Source: https://nilsonreport.com/articles/card-fraud-losses-worldwide-in-2023/
Why Crypto On-Ramps and Fiat Gateways Are Prime Payment Fraud Targets
Crypto on-ramps sit on a dangerous asymmetry: money flows in through reversible instruments (cards, ACH) but flows out as an irreversible blockchain transfer. Providers like MoonPay, Transak, and Ramp bridge these two systems and absorb the mismatch. A fraudster pays with something that can be clawed back and receives something that cannot.
That asymmetry is why crypto is a preferred cash-out for stolen funds. In its 2023 Cryptocurrency Fraud Report (released September 2024), the FBI's Internet Crime Complaint Center (IC3) recorded more than $5.6 billion in crypto-related fraud losses, up roughly 45% year over year, and named the speed and irreversibility of on-chain transfers as a core reason criminals favor crypto. Source: https://www.ic3.gov/AnnualReport/Reports/2023IC3CryptocurrencyReport.pdf_
Stolen Cards Buying Crypto: Card-Not-Present and Card Testing Fraud
Card-not-present (CNP) fraud happens when a stolen card number is entered online without the physical card. At an on-ramp, the fraudster funds a purchase, converts it to crypto, and withdraws on-chain. Because the transfer cannot be reversed, the real cardholder later files a chargeback and the on-ramp eats the loss.
Yes, you can buy crypto with a stolen credit card if a gateway's controls fail, which is exactly why detection is front-loaded. Attackers rarely start big. Card testing probes stolen numbers with tiny charges, often automated across many cards, to confirm which are live before a large buy. A burst of small authorizations and declines from one device is a classic tell.
First-Party (Friendly) Fraud: When the Chargeback Is the Attack
First-party or friendly fraud is when a genuine cardholder makes a legitimate crypto purchase, then disputes the charge with their bank to reclaim the fiat while keeping the crypto. It weaponizes chargeback rules that were written for undelivered or defective goods, not for an asset that has already settled on another ledger.
Can you charge back a crypto purchase? At the card layer, yes, a cardholder can open a dispute, and banks often side with the customer. But the on-ramp cannot pull the crypto back on-chain, so the disputed amount is a direct loss. This makes chargeback (friendly) fraud one of the hardest categories to fight after the fact.
Account Takeover and Other Payment Fraud Vectors at On-Ramps
Account takeover (ATO) is when an attacker gains control of a victim's exchange or on-ramp account, often through phishing or credential stuffing, and uses stored payment methods to buy crypto. Related vectors include stored-payment abuse, phishing-funded buys, and triangulation or refund fraud. Each ends in the same place: an irreversible on-chain withdrawal.
The shared pattern is that a legitimate-looking payment session masks a stolen identity or stolen funds. Signals worth watching include a login from a new device or country, a changed withdrawal wallet immediately before a large buy, and a mismatch between the refund destination and the original payer.
Common Types of Payment Fraud at a Crypto On-Ramp
The most common type of payment fraud at gateways is card-not-present fraud, because it scales cheaply and needs no physical card. The table below maps each major type to how it works, who absorbs the loss, and the signal that best exposes it before settlement.
| Fraud type | How it works | Who eats the loss | Primary detection signal |
|---|---|---|---|
| Card-not-present (CNP) | Stolen card number entered online to buy crypto | On-ramp, after chargeback | BIN and issuer-geo mismatch, device fingerprint |
| Card testing | Micro-charges validate live stolen cards before a big buy | On-ramp, plus processor fees | Velocity spikes, many declines from one device |
| Chargeback / friendly fraud | Real cardholder disputes a legitimate crypto buy | On-ramp, crypto already settled | Dispute history, prior chargebacks, account age |
| Account takeover (ATO) | Attacker logs into a victim's account and buys | Victim and on-ramp | New device or geo login, changed payout wallet |
| Triangulation / refund fraud | Fake refund or third-party order routes funds out | Merchant and cardholder | Mismatched refund destination, fresh wallet |
Warning Signs of a Risky Payment Before Settlement
The strongest warning signs cluster around newness and mismatch. No single flag is proof, but several together sharply raise the probability that a payment is fraudulent and should be held for review before any crypto is released to the destination wallet.
- Fresh account making a high-value first purchase
- Device or geolocation that does not match the billing country
- Rapid velocity: many attempts or cards in a short window
- New or sybil-like destination wallet with little real history
- Disposable or throwaway email address
- Card BIN whose issuer geography contradicts the customer's stated location
How On-Ramps Detect Payment Fraud Before Irreversible On-Chain Settlement
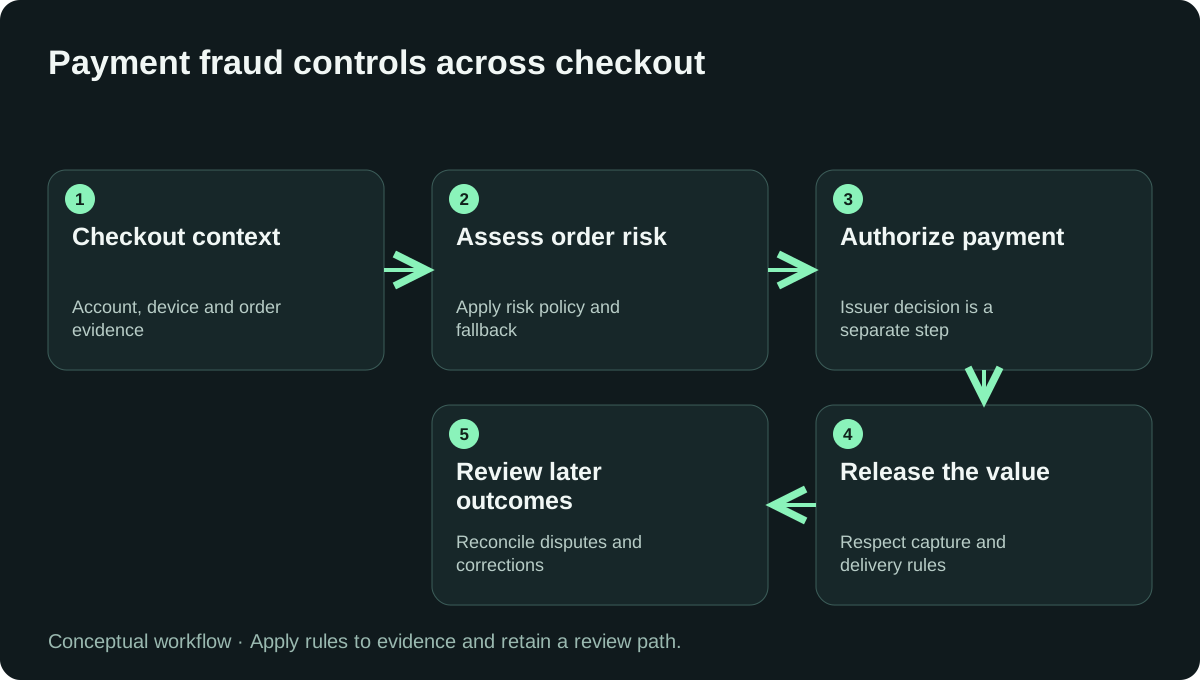
On-ramps detect fraud with a layered stack rather than one control. The layers are KYC and identity checks, 3-D Secure (3DS) authentication, device and browser fingerprinting, velocity and geolocation rules, card BIN and issuer signals, and destination-wallet reputation. Each layer catches a different attack, and the crypto is released only after they clear.
Risk teams evaluating this stack usually start from a comparison of payment fraud detection tools before deciding which vendors to combine, since the CNP layer, the authentication layer, and the on-chain layer are rarely served well by a single product. The goal is to score the transaction while it is still reversible and hold anything suspicious for step-up verification or manual review.
On-Chain Reputation and Proof-of-Human: Screening the Destination Wallet
The one signal card and device tools cannot see is the wallet receiving the crypto. On-chain reputation fills that gap by scoring the destination address by its real, cumulative history across many blockchains, separating an established human user from a fresh wallet spun up by a cash-out ring.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
Reducing Payment Fraud Exposure: A Layered Detection Playbook
No single control wins. Reducing exposure means combining authentication, behavioral and device signals, velocity limits, staged withdrawals, and on-chain reputation into one decision, then acting before the crypto is released rather than after the chargeback lands. Detection has to beat blockchain finality, not chase it.
- Authenticate the payer with KYC and 3-D Secure on higher-risk transactions.
- Fingerprint the device and browser to catch reused or spoofed sessions.
- Apply velocity and geolocation rules to expose card testing and mismatch.
- Score the destination wallet with on-chain reputation and proof-of-human checks.
- Stage large first withdrawals with holds or step-up review while risk is still reversible.
Ecommerce payment fraud and chargeback evidence
Ecommerce payment fraud controls need the order, payment, delivery and subsequent dispute record. Account and device observations can add context, but they cannot independently determine card authorization or guarantee a chargeback outcome. Compare the payment methods and controls actually supported by the provider.
Place a review before fulfillment when a hold can still protect value. Keep first-party disputes, stolen-payment instruments and instrumentation errors in separate outcome categories. A later dispute must not silently become proof that every related account was fraudulent at signup.
For implementation context, see payment-fraud prevention and payment gateway fraud guide. Related editorial sources include Medium comparison of ecommerce fraud tools. Read next: best fraud detection apis developers 2026, fraud prevention workflows.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best Ecommerce Fraud Prevention Tools in 2026.
Frequently Asked Questions
What is payment fraud? Payment fraud is any transaction that uses stolen, falsified, or unauthorized payment information to obtain money, goods, or services. Common forms include card-not-present fraud, chargeback (friendly) fraud, account takeover, and card testing. At crypto on-ramps it is especially damaging because the fiat payment can be reversed while the crypto it buys settles on-chain and cannot be clawed back.
How do stolen cards get used to buy crypto? Fraudsters enter stolen card numbers in card-not-present transactions at a crypto on-ramp, convert the balance into cryptocurrency, and withdraw it to a wallet they control. Because on-chain transfers cannot be reversed, the real cardholder later files a chargeback and the on-ramp absorbs the loss. Attackers often card test small amounts first to confirm a stolen card is live before a larger buy.
What is first-party (friendly) fraud in crypto payments? First-party or friendly fraud is when a genuine cardholder makes a legitimate crypto purchase, then disputes the charge with their bank to reclaim the fiat while keeping the crypto. It abuses chargeback rules meant for undelivered goods. Because the crypto has already settled on-chain, the on-ramp cannot recover it and eats the disputed amount.
Why is payment fraud at crypto on-ramps so hard to reverse? Card and bank payments can be disputed and reversed for months, but blockchain transactions settle with finality and have no chargeback mechanism. This asymmetry lets a fraudster pay with a reversible instrument, receive an irreversible asset, and move it out before the dispute lands. Detection therefore has to happen before the crypto is released, not after.
How do crypto on-ramps detect fraudulent payments? On-ramps combine KYC and identity checks, 3-D Secure authentication, device and browser fingerprinting, velocity and geolocation rules, card BIN and issuer signals, and on-chain reputation scoring of the destination wallet. Together these flag risky payments, such as a fresh account making a high-value first buy or a wallet with sybil-like history, before the transaction is approved and settled.
Can on-chain reputation help prevent payment fraud? Yes. On-chain reputation scores a destination wallet by its real, cumulative activity across many blockchains, distinguishing established human users from fresh or sybil wallets tied to fraud rings. RubyScore's Multichain Reputation Score and Proof-of-Human ID give on-ramps a wallet-side risk signal that complements card and device checks, adding a layer traditional payment fraud tools cannot see.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] payment-fraud prevention — vendor product scope.
[2] payment gateway fraud guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for payment fraud prevention
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs demo: Payment Fraud Prevention Test | Inspect this controlled workflow example; do not treat a demo as a production accuracy benchmark. |
| ShieldLabs documentation: Checkout risk | Relate this scenario to the application action, qualification rule and later outcome record. |
| How to prevent guest checkout fraud | Background on What is guest checkout fraud?. Verify implementation details in the primary references. |
| ShieldLabs payment fraud research archive | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


