
New Account Fraud Prevention: Signups, Benefits and Wallet Risk
New Account Fraud Prevention: Signups, Benefits and Wallet Risk. Compare evidence, practical controls and limitations, with related implementation sources.
New account fraud prevention evaluates the risk of a registration and its first valuable action. Signup context, account relationships and benefit history can expose repeated claims, but a fresh account or wallet is not inherently fraudulent. Distinguish unknown users from confirmed abuse and verify eligibility before releasing credits, access or rewards.
This guide explains how new account fraud works, why brand-new wallets are the Web3 version of the problem, and how protocols score a fresh wallet before it ever touches a reward pool.
What Is New Account Fraud?
New account fraud, also called account creation fraud, occurs when a fraudster opens a new account using stolen, synthetic, or fabricated identity data to exploit a system. The goal is to extract value — credit, promotions, or tokens — before the platform detects that the account does not belong to a real, unique user.
Synthetic identity fraud is a close cousin. Instead of stealing a whole identity, the fraudster stitches together real and fake data to manufacture a person who does not exist.
The scale is not trivial. The Federal Trade Commission reported that U.S. consumers lost more than $12.5 billion to fraud in 2024, a 25% jump over the prior year. That figure covers all reported consumer fraud rather than new-account fraud alone, but it shows the scale of the problem. Source: https://www.ftc.gov/news-events/news/press-releases/2025/03/new-ftc-data-show-big-jump-reported-losses-fraud-125-billion-2024
How New Account Fraud Shows Up in Web3: The Fresh-Wallet Problem
In Web3, new account fraud rarely involves stolen names or documents. It shows up as waves of freshly created wallets, spun up in bulk and scripted to look like independent users. Each wallet is a disposable "new account" built to claim rewards, complete quests, or qualify for an airdrop, then discarded.
A wallet address is free and permissionless to create. That is a feature for real users and a weapon for fraudsters.
One person can control thousands of wallets from a single machine. When a protocol treats each address as a distinct human, it hands the same reward to the same actor thousands of times over.
Why Brand-New Wallets Are High-Risk at Onboarding
Brand-new wallets are high-risk because they carry no transaction history, so there is no on-chain evidence that a real human controls them. Without a track record of genuine activity, a fresh address is indistinguishable from one of a thousand scripted clones — which is exactly why wallet age and activity depth are core onboarding signals.
Wallet age is the time elapsed since an address first transacted on-chain. A wallet minted minutes before a claim has no history to trust.
Legitimate users usually arrive with a footprint: swaps, bridges, NFT mints, prior dApp use. Fraud wallets arrive empty and purpose-built, which is the signal defenders lean on.
How Fraudsters Exploit New Wallets in Airdrops, Quests, and Reward Programs
Fraudsters exploit new wallets through sybil attacks and airdrop farming: they create many fresh addresses, run each through the minimum actions needed to qualify, and multiply a single reward into thousands of payouts. Quest platforms and airdrops are the prime targets because eligibility is often based on wallet-level activity that scripts can fake.
A sybil attack is when one entity operates many fake identities to gain disproportionate influence or rewards.
Airdrop farming is the practice of manufacturing activity across many wallets purely to qualify for a token distribution, with no intent to use the protocol.
The problem is measurable at scale. In its 2024 airdrop review, LayerZero published a preliminary list of 803,093 wallet addresses flagged as potential sybils, noting that addresses could be removed as the analysis was refined. Source: https://crypto.news/layerzero-spots-800k-sybil-addresses-airdrop-scheme/
Red Flags: How to Spot a High-Risk New Wallet
The clearest red flags are wallets created moments before claiming, shared funding sources across many addresses, and scripted, uniform behavior. Individually, any one signal can be innocent. Clustered together across a batch of wallets, they are the fingerprint of coordinated sybil farming rather than organic user growth.
Watch for these patterns during onboarding:
- Just-in-time creation — the wallet was funded and activated minutes before the reward claim.
- Zero prior dApp interactions — no swaps, bridges, or contract calls before the qualifying action.
- Shared funding lineage — dozens or hundreds of wallets financed from one source address or exchange withdrawal.
- Scripted timing — transactions fire at uniform intervals no human would produce.
- Coordinated movement — funds fan out and reconverge in tightly clustered patterns.
- Single-purpose history — the wallet only ever performed the exact actions the campaign rewards.
New Account Fraud vs. Account Takeover: What Is the Difference?
New account fraud creates a fresh fraudulent account from scratch to abuse a system, while account takeover (ATO) hijacks an existing legitimate account. Onboarding controls and reputation scoring target the former; authentication, key security, and session monitoring target the latter. The defenses barely overlap, so protocols need both.
| Dimension | New Account Fraud | Account Takeover (ATO) |
|---|---|---|
| Target | A newly created account or wallet | An existing, legitimate account or wallet |
| Web3 form | Fresh wallets farming rewards | Compromised keys or seed phrase draining a real wallet |
| Attacker goal | Multiply claims and extract rewards | Steal assets from a genuine owner |
| Strongest signal | Wallet age and activity depth | Anomalous access and sudden behavior change |
| Primary defense | Onboarding reputation scoring | Authentication and key or session monitoring |
How to Score a Fresh Wallet Before Granting Access or Rewards
Score a wallet by aggregating on-chain signals — wallet age, transaction count, contract diversity, cross-chain activity, and funding lineage — into a single reputation score, then set a threshold below which the wallet must complete additional verification before receiving anything. This turns a binary "new or old" check into a graded risk decision.
A reputation score compresses years of on-chain behavior into one number a protocol can act on at onboarding.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
On-chain scoring is only one layer, and because signup-time defenses vary widely, many teams weigh options through an roundup of new-account-fraud prevention tools before wiring a threshold into their claim flow. Catching a fake at creation time is far cheaper than clawing back tokens after distribution.
On-Chain Signals That Separate Real Users From Bots and Sybils
The signals that separate real users from bots are behavioral depth and diversity that scripts cannot cheaply fake: a long wallet age, varied contract interactions across many chains, organic transaction timing, and independent funding. Bots and sybils optimize for the minimum viable footprint, and that thinness is itself the tell.
Protocols weigh signals such as:
- Wallet age — how long the address has genuinely transacted.
- Transaction depth — count and variety of real interactions, not just the qualifying action.
- Contract diversity — engagement with many distinct protocols, not one script.
- Cross-chain activity — a footprint spread across ecosystems, which RubyScore reads across 70+ chains.
- Funding lineage — whether the wallet is financed independently or from a shared sybil source.
- Behavioral entropy — human-like irregularity in timing versus machine uniformity.
An on-chain attestation can make a recorded claim available to a receiving application. Acceptance, eligibility thresholds and ecosystem scope still depend on that application. A published score is not an automatic guarantee of transparent computation, universal portability or unique-person identity.
Best Practices to Prevent New Account Fraud in Web3 Onboarding
The best defense is to gate rewards behind a reputation threshold rather than a simple wallet check, then escalate verification only for low-scoring addresses. Combine automated on-chain scoring with proof-of-human identity, weight wallet age and cross-chain depth heavily, and monitor continuously instead of trusting a one-time signup snapshot.
Practical steps for protocol, airdrop, and quest teams:
- Score before you reward. Require a minimum reputation score to qualify, computed from on-chain history.
- Set thresholds with step-up verification. Let high-reputation wallets pass; route low scores to extra checks.
- Weight age and depth. Treat a wallet's genuine history as the hardest signal to fake.
- Read cross-chain, not single-chain. A wallet thin on one chain may be rich elsewhere, and vice versa.
- Detect clusters, not just wallets. Shared funding and coordinated timing expose sybil rings a per-wallet view misses.
- Pair scoring with proof-of-human. Reputation plus identity filters bots without collecting personal documents.
- Monitor after onboarding. Behavior that turns adversarial post-signup still needs to be caught.
Can new account fraud be prevented without collecting personal identity documents? Yes. On-chain reputation and proof-of-human systems assess real wallet activity across many blockchains rather than KYC files, preserving user privacy and self-custody.
Fake account prevention before the first benefit
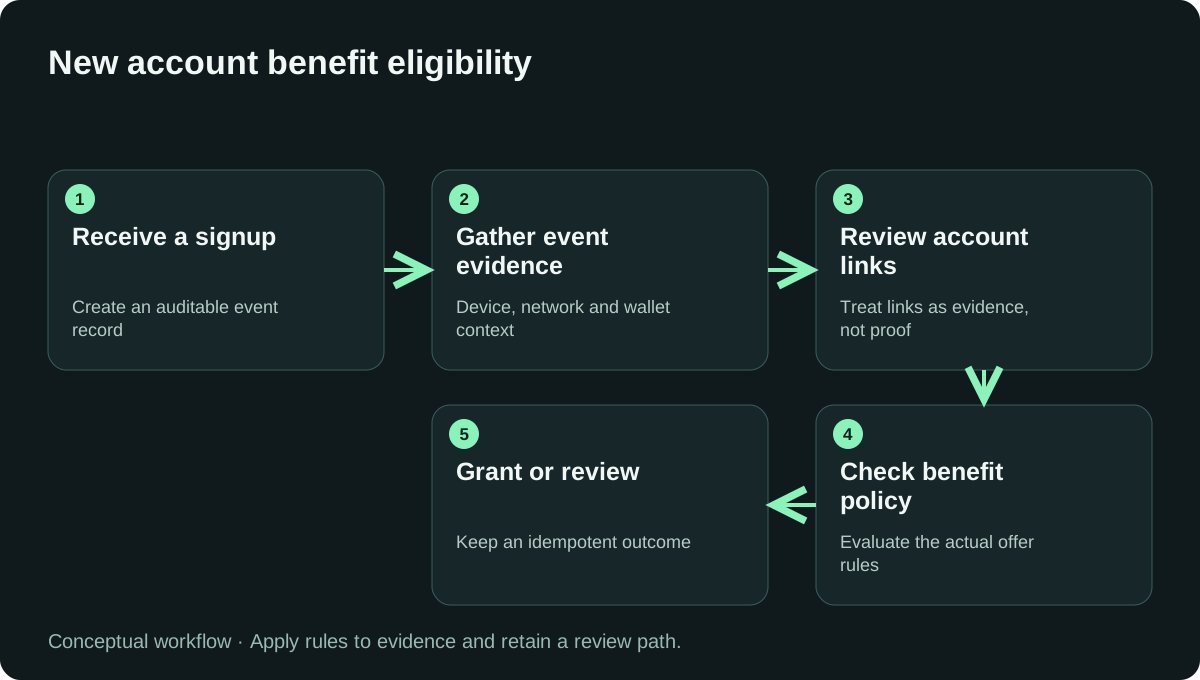
Fake account prevention should distinguish registration quality from entitlement. A verified inbox, a clean-looking IP or a new wallet does not prove that a participant is independently eligible. Equally, a new user with little history should not be presumed fraudulent.
Join signup evidence to the first trial, discount, referral or other benefit. Keep missing data explicit, use server-controlled action identifiers and review repeated-beneficiary patterns. Reconcile later account and payment outcomes so a pilot does not count unreviewed alerts as confirmed fraud.
For implementation context, see new-account fraud controls and new-account workflow guide. Related editorial sources include Medium guide to stopping new-account fraud at signup, Medium shortlist of fake-signup detection tools. Read next: synthetic identity fraud signals, free trial abuse crypto.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best New Account Fraud Prevention Tools in 2026.
Frequently Asked Questions
What is new account fraud?
New account fraud occurs when someone opens an account using stolen, synthetic, or fabricated details to gain access to something valuable. In Web3, the same pattern appears as freshly created wallets used to farm rewards, quests, and airdrops without belonging to a real, unique user.
Why are brand-new wallets considered high-risk at onboarding?
Brand-new wallets carry no transaction history, so there is no on-chain evidence that a real human controls them. Attackers spin up thousands of fresh wallets to multiply reward and airdrop claims, which makes wallet age and activity depth core risk signals during onboarding.
What are the red flags of new account fraud in reward and quest programs?
Common red flags include wallets created minutes before claiming, identical funding sources shared across many addresses, no prior dApp interactions, scripted transaction timing, and clusters of wallets that move funds in tightly coordinated patterns typical of sybil farming.
How do you score a new wallet before granting access or rewards?
Score a wallet by aggregating on-chain signals such as wallet age, transaction count, contract diversity, cross-chain activity, and funding lineage into a single reputation score, then set a threshold below which the wallet must complete additional verification before receiving rewards.
What is the difference between new account fraud and account takeover?
New account fraud creates a fresh fraudulent account from scratch to abuse a system, while account takeover hijacks an existing legitimate account. Onboarding controls and reputation scoring target the former; authentication and session monitoring target the latter.
Can new account fraud be prevented without collecting personal identity documents?
Yes. On-chain reputation and proof-of-human systems assess a wallet's real activity across many blockchains rather than relying on KYC documents, filtering bots and sybil farmers while preserving user privacy and self-custody.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] new-account fraud controls — vendor product scope.
[2] new-account workflow guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for fake account prevention
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs demo: New Account Fraud Prevention Test | Inspect this controlled workflow example; do not treat a demo as a production accuracy benchmark. |
| ShieldLabs documentation: New account fraud | Relate this scenario to the application action, qualification rule and later outcome record. |
| The 8 best new-account fraud detection tools in 2026 | Background on What is new-account fraud detection?. Verify implementation details in the primary references. |
| Four Stage Risk Funnel for Fake Signup Detection with Persistent ID | Background on What Is Fake Signup Detection?. Verify implementation details in the primary references. |
| ShieldLabs account abuse research archive | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| ShieldLabs account abuse research archive — page 2 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
| ShieldLabs account abuse research archive — page 3 | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


