
Account Takeover Detection: Logins, Sessions and Crypto Risk
Account Takeover Detection: Logins, Sessions and Crypto Risk. Compare evidence, practical controls and limitations, with related implementation sources.
Account takeover detection investigates whether an unauthorized actor controls an existing account or session. Authentication history, device context and sensitive changes can provide evidence. In crypto, distinguish an exchange-account compromise, a stolen wallet key and a malicious contract approval: they can cause similar losses while requiring different preventive and recovery controls.
The stakes are not abstract. The FBI's Internet Crime Complaint Center logged 149,686 cryptocurrency-related complaints in 2024 with reported losses exceeding $9.3 billion, a 66% jump over the prior year. Account takeover fraud is one slice of that landscape, and it is among the fastest to complete once a key or session is compromised.
Source: https://www.ic3.gov/AnnualReport/Reports/2024_IC3Report.pdf
What Is Crypto Account Takeover?
Account takeover (ATO) is when an attacker seizes control of an existing account you own, rather than opening a new one in your name. In crypto, "account" means one of two things: a login on a centralized exchange, or a self-custody wallet controlled by a private key or seed phrase. Once the attacker controls the credentials, keys, or session, they operate the account as if they were you.
A common account takeover example: a user receives a fake "wallet migration" prompt, enters their 12-word seed phrase on a lookalike site, and within minutes the attacker imports that wallet elsewhere and sweeps every token. The user still holds their device and password, but control of the funds is already gone. When someone takes over your account this way, the plain term for it is exactly that: account takeover, often shortened to ATO.
Exchange Accounts vs. Self-Custody Wallets: Two Different Attack Surfaces
The two account types fail in different ways, and the response differs sharply.
- Centralized exchange account: protected by a password plus multi-factor authentication (MFA). Attackers target login credentials, session tokens, API keys, and phone numbers (via SIM-swap). Because the exchange custodies your assets, it can sometimes freeze the account or halt a withdrawal if you act fast.
- Self-custody wallet: protected by a private key or seed phrase. Attackers target the key itself or trick you into signing a transaction or a malicious token approval. There is no help desk and no freeze button. Whoever holds the key holds the funds.
That difference is why wallet hijacking of a self-custody wallet is treated as an emergency: the recovery window on a custodial platform is measured in hours, while on-chain it is often measured in seconds.
How Crypto Wallets Get Hijacked: The Main Attack Vectors
Hackers gain access through a handful of repeatable techniques:
- Phishing and fake dApps: lookalike sites and malicious "connect wallet" prompts that harvest seed phrases or trick you into signing a draining transaction.
- Seed phrase theft and private-key theft: clipboard malware, infostealers, screenshots synced to the cloud, or a fake "support agent" who asks you to "verify" your phrase.
- Malicious token approvals and wallet drainers: a single signature that grants a contract permission to move your tokens later, no further confirmation needed.
- Session hijacking on exchange accounts: stolen session cookies or tokens let an attacker act inside a logged-in session, sometimes bypassing the password step entirely. A session hijacking wallet-adjacent attack on an exchange can change withdrawal settings before you notice.
- SIM-swap attacks: the attacker ports your phone number to their SIM, intercepts SMS one-time codes, and resets passwords. This is why SMS-based 2FA is the weakest option.
Most real-world incidents chain two or more of these together, for example a phishing link that installs malware that then reads the seed phrase.
What a Malicious Token Approval Is and Why It Is So Dangerous
A malicious token approval is a transaction that grants a smart contract permission to move your tokens. On ERC-20 tokens this is the approve() function; on NFTs and token collections it is setApprovalForAll. Legitimate dApps request a limited, specific approval. Scam contracts request unlimited access or approval over an entire collection, so the attacker can transfer your assets at any later time without asking you to sign again.
This is what makes drainers efficient: the victim signs once, sees nothing leave immediately, and the contract quietly sweeps the wallet minutes or days later. You can audit and cancel these permissions with a revocation tool or a block explorer's approval checker, and security auditors have long flagged unlimited approvals as a standing risk. Reviewing approvals should be routine hygiene, not a one-time cleanup.
Source: https://revoke.cash Source: https://etherscan.io/tokenapprovalchecker
Why On-Chain Account Takeover Is Often Irreversible
Public blockchains settle transactions with finality. There is no issuer to reverse a charge, no chargeback, and no central authority that can undo a confirmed transfer. When an attacker moves assets out of a self-custody wallet, those transactions are permanent. This is the core reason a crypto wallet hacked at the key level is treated as a total loss of the moved funds.
Exchange accounts sit slightly differently. Because a centralized platform custodies the assets, it may be able to freeze the account, block a pending withdrawal, or flag the destination, but only if you and the platform act inside a very narrow window. The lesson is the same in both cases: prevention and early detection matter far more than after-the-fact recovery.
Warning Signs: How Behavioral and On-Chain Signals Reveal a Takeover
A takeover almost always produces activity that breaks the wallet's established pattern. The clearest red flags:
- A sudden token approval to an unknown or freshly deployed contract.
- Outbound transfers to newly created addresses with no prior relationship to the wallet.
- A full-balance sweep, especially of long-held assets.
- A signature or exchange login from a new device, browser, or geography.
- Withdrawal-address or API-key changes on an exchange you did not initiate.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
ATO Vector to Warning Sign to Mitigation
| Attack vector | Typical warning sign | Primary mitigation |
|---|---|---|
| Phishing / fake dApp | Signature request from an unfamiliar domain; approval to an unknown contract | Verify URLs before connecting; use a hardware wallet; simulate transactions |
| Seed-phrase / private-key theft | Full-balance sweep to a brand-new address | Never enter your seed online; store it offline; move funds to a fresh wallet if exposed |
| Malicious token approval | setApprovalForAll or unlimited approve() to an unknown spender | Grant limited approvals; revoke unused ones with Revoke.cash or a block explorer |
| Session hijacking (exchange) | Withdrawal or API-key change from a new IP or device | Phishing-resistant MFA; short sessions; withdrawal allowlists |
| SIM-swap attack | SMS codes stop arriving; a password reset you did not request | Use an authenticator app or hardware key, not SMS; set a carrier port-out lock |
Layered Defenses: Hardware Wallets, Approval Hygiene, and Monitoring
NIST SP 800-63B-4 distinguishes phishing-resistant authentication from ordinary one-time codes. Evaluate the method supported by the service and its recovery process.
No single control stops account takeover fraud, so effective protection stacks several:
- Hardware wallets (Ledger, Trezor): keep the private key off internet-connected devices, so malware cannot read it.
- Approval hygiene: grant only limited token approvals, and revoke unused ones on a schedule.
- Phishing-resistant MFA: a supported passkey or FIDO security key on exchange accounts. One-time codes from authenticator apps add a factor but are not themselves phishing-resistant.
- URL and connection discipline: verify dApp domains, bookmark the real ones, and treat WalletConnect prompts and MetaMask or Trust Wallet signature requests as high-stakes decisions.
- Monitoring and alerts: real-time alerts on approvals and outbound transfers give you the chance to react before a wallet is drained.
Because these controls span keys, credentials, and behavior, many teams benchmark their stack against an overview of account-takeover prevention tools before choosing a monitoring vendor, rather than assuming one product covers every surface. Exchange-side platforms increasingly layer behavioral and device fraud detection as well; vendors such as Sardine build signals to catch logins and withdrawals that do not match a user's history.
How to Spot a Takeover Early and What to Do in the First Minutes
If you suspect a takeover, speed matters more than certainty. Act as if it is real:
- Move remaining assets to a new, previously unused wallet you fully control, if the private key or seed may be exposed.
- Revoke active approvals on every affected chain so a drainer contract cannot pull more tokens.
- On an exchange, lock it down: freeze the account if possible, rotate the password, revoke API keys, and contact support immediately.
- Preserve evidence: record transaction hashes, destination addresses, and timestamps.
- Report it: in the US, file with the FBI's IC3, and notify the exchange, which may be able to flag or freeze the destination.
The wallets that survive are usually the ones with monitoring in place, because the owner got an alert on the first abnormal approval instead of discovering the loss hours later.
Can You Recover a Hijacked Wallet or Account?
For self-custody wallets, usually not. On-chain transfers are irreversible, so funds already moved are generally gone, and any wallet whose seed phrase is compromised should be abandoned entirely, with remaining assets migrated to a new one. For exchange accounts there is more hope: because the platform custodies funds, contacting the exchange and law enforcement quickly can occasionally freeze an account or block a withdrawal. Knowing how to prevent account takeover in the first place remains far more reliable than any recovery path.
Account takeover signals and credential-stuffing prevention
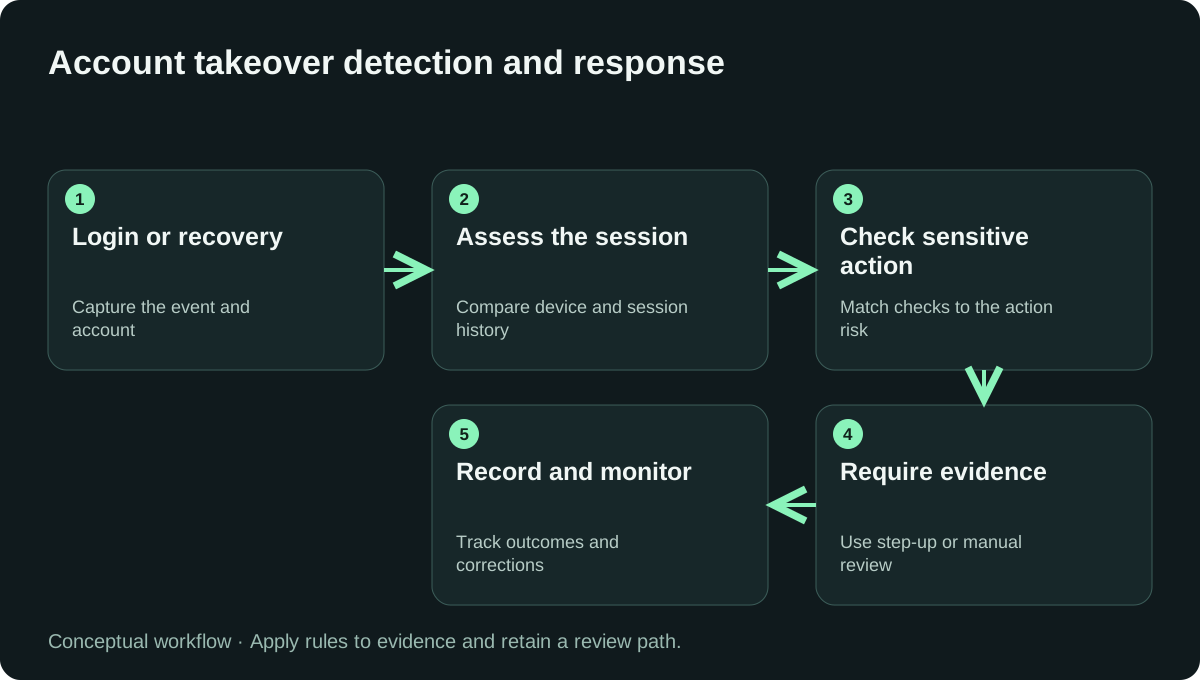
Account takeover signals are useful at login and again before sensitive changes. Credential stuffing abuses valid username/password combinations, while recovery abuse may bypass the normal login path. Successful authentication does not establish that a later payout or security change should be trusted.
Join session history, authentication evidence, device context and account changes. Treat unfamiliar travel or a new device as context rather than proof. Use step-up authentication and a recovery process appropriate to the action, and record confirmed compromise separately from unresolved alerts.
For implementation context, see account-takeover prevention and account-takeover signal guide. Related editorial sources include Medium comparison of account takeover prevention tools. Read next: synthetic identity fraud signals, best fraud detection apis developers 2026.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best Account Takeover Prevention Tools in 2026.
Frequently Asked Questions
How do crypto wallets get hijacked? Crypto wallets are hijacked mainly through phishing sites and fake dApps, seed-phrase or private-key theft (often via malware or fake support agents), malicious token approvals that grant a contract spending rights, and session or SIM-swap hijacks on exchange accounts. Once a key or approval is compromised, an attacker can move assets directly on-chain.
What is a malicious token approval? A malicious token approval is a transaction that grants a smart contract permission to move your tokens. Legitimate dApps request limited approvals, but scam contracts request unlimited access (often via setApprovalForAll or a very high approve() amount), letting the attacker transfer your tokens later without another signature. You can review and revoke approvals with tools like Revoke.cash or a block explorer.
Can you recover a hijacked crypto wallet? Usually no. On-chain transactions are irreversible, so funds moved out of a self-custody wallet generally cannot be reversed. If a seed phrase is compromised, move remaining assets to a brand-new wallet immediately and stop using the old one. For exchange accounts, contact the exchange and law enforcement (in the US, the FBI's IC3) right away, since custodial platforms may be able to freeze the account.
How do you spot a crypto account takeover early? Watch for activity that breaks the wallet's established on-chain pattern: sudden token approvals to unknown contracts, transfers to freshly created addresses, signatures or logins from a new device or geography, and unexpected outbound transactions. Real-time monitoring and alerts on approvals and transfers give the best chance to react before assets are drained.
How can you avoid account takeover in crypto? Use a hardware wallet for significant holdings, use a supported phishing-resistant method such as a passkey or FIDO security key on exchanges, verify dApp URLs before connecting, grant only limited token approvals and revoke unused ones, and never enter your seed phrase on a website. Monitoring that alerts on abnormal activity adds a detection layer on top of good hygiene.
Is account takeover a form of identity theft? Account takeover is closely related to identity theft but not identical. In ATO, an attacker seizes control of an existing account (such as a crypto exchange or wallet) using stolen credentials, keys, or session tokens, then uses it for fraud. Identity theft more broadly involves impersonating a victim to open new accounts or commit fraud in their name.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] account-takeover prevention — vendor product scope.
[2] account-takeover signal guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for account takeover detection signals
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs demo: Account Takeover Prevention Test | Inspect this controlled workflow example; do not treat a demo as a production accuracy benchmark. |
| ShieldLabs documentation: Account takeover | Use the scenario to plan an integration test; a published example is not a test result from your application. |
| ShieldLabs documentation: Account takeover | Relate this scenario to the application action, qualification rule and later outcome record. |
| The 14 best account takeover detection tools in 2026 | Background on What is account takeover detection?. Verify implementation details in the primary references. |
| ShieldLabs account takeover research archive | Navigate the publication archive and inspect the dates and primary sources of relevant articles. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


