
Airdrop Farming Rings: Wallet Clusters and Multi-Accounting Evidence
Airdrop Farming Rings: Wallet Clusters and Multi-Accounting Evidence. Compare evidence, practical controls and limitations, with related implementation sources.
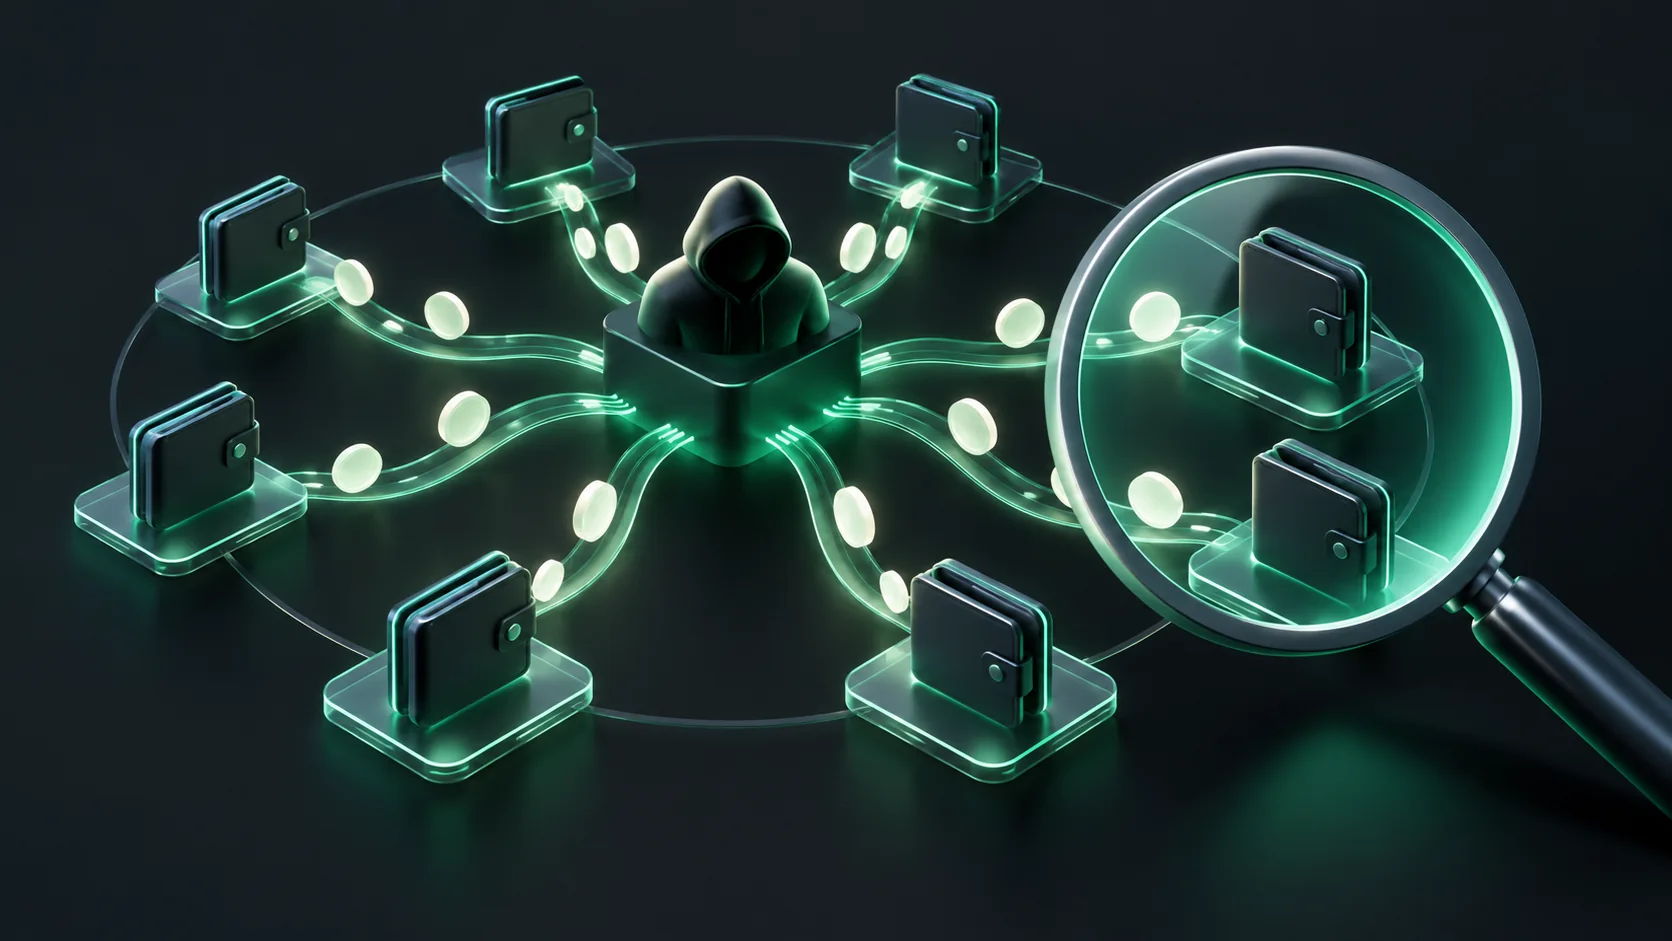
An airdrop farming ring is a coordinated operation using multiple wallets to seek allocations intended for independent participants. Funding, timing, transaction and device relationships can identify clusters for review. Those observations support an eligibility investigation; they do not by themselves prove a person count or establish that every linked wallet violated the campaign rules.
What Is an Airdrop Farming Ring? (And Why It's a Sybil Problem)
An airdrop farming ring is the industrial version of airdrop hunting. Instead of one person completing tasks with one wallet, an operator spins up a fleet of addresses that each perform the minimum activity needed to qualify, then collect a proportional share of the reward pool.
That is textbook Sybil behavior. A Sybil attack is when one entity forges many identities to gain influence a single identity could not. In Web3, "identity" is a wallet address, and creating a new one is free and permissionless. So the same property that makes crypto open also makes it trivially exploitable: nothing stops one human from presenting as ten thousand wallets.
Sybil attacks show up in several forms — governance vote manipulation, consensus attacks on small networks, quest-platform reward farming, and airdrop farming. Airdrop farming is the most common and most profitable variant, because token distributions convert fake activity directly into liquid value. The result: genuine users get diluted, and token distribution skews toward whoever ran the largest ring.
How One Operator Runs Hundreds of Wallets: Funding, Scripting, and Bridging
Running a ring is an operational problem, and operators optimize for cost and throughput. A typical setup follows a repeatable pattern:
- Fund at scale. Wallets are seeded from a shared source — usually a centralized exchange (CEX) withdrawal, a hot wallet, or a distribution contract — often within a tight time window.
- Script the activity. Automation pushes each wallet through the same sequence of swaps, bridges, and contract calls, tuned to hit whatever the airdrop criteria are rumored to reward.
- Bridge to target chains. Cross-chain bridges move small, similar amounts through the same routes so every wallet shows "multichain" activity cheaply.
- Sweep after the snapshot. Once the qualifying snapshot passes, funds and eventually tokens are consolidated back to a few collection wallets.
The efficiency that makes this profitable is also its weakness. Scripts produce uniformity, and uniformity is exactly what analysts hunt for.
Authentic User vs. Farming Ring: The On-Chain Signals Compared
Real usage is messy; scripted usage is clean. Wallet clustering works because farming rings leave a statistically obvious fingerprint across their addresses. The contrast is stark when you line up the signals side by side.
| Signal | Authentic User | Farming Ring Wallet |
|---|---|---|
| Funding source | Unique, personal CEX withdrawal | Shared source funding many wallets |
| Interaction sequence | Irregular, exploratory | Identical scripted steps across wallets |
| Timing | Spread over weeks or months | Clustered in tight windows, often the same hour |
| Chain coverage | Follows real needs | Uniform minimum-viable actions on target chains |
| Gas and fees | Varied, occasional failed txs | Optimized, near-identical patterns |
| Bridging | As needed, varied amounts | Same bridge, similar amounts, batched |
| Capital at risk | Ongoing balances | Minimum viable, swept after snapshot |
| Post-airdrop behavior | Keeps using the protocol | Dumps tokens, abandons wallets |
No single row proves fraud. A cluster becomes a case when multiple rows line up across dozens or hundreds of wallets at once.
The Detection Playbook: Funding-Graph, Temporal Clustering, and Humanness Scoring
How to detect airdrop Sybils comes down to three layered techniques, usually run together:
- Funding-graph analysis. Trace each wallet's money back to its origin. When hundreds of addresses share one CEX account, hot wallet, or bridge source, graph mining surfaces the tree connecting them. This is the highest-signal method because funding is expensive to fully randomize.
- Temporal and behavioral clustering. Group wallets by when and how they act. Synchronized timing, identical contract-call ordering, matching bridge amounts, and copy-paste gas usage all bind scripted wallets together even when funding is obscured.
- Humanness and reputation scoring. Score each wallet on the depth, age, and organic variety of its on-chain history. A wallet that only exists to farm looks nothing like one with years of independent, non-scripted activity.
Because these methods overlap, teams building their own defenses often start by scanning an comparison of multi-accounting prevention tools before narrowing down to the on-chain-specific signals above. The stack matters: funding graphs catch the lazy rings, temporal clustering catches the medium-effort ones, and reputation scoring raises the cost for the sophisticated operators who evade the first two.
Case Studies: What LayerZero and ether.fi Learned Filtering Sybils
The two most documented Sybil-filtering operations in airdrop history validate this playbook.
LayerZero ran its pre-launch Sybil detection with analytics firm Nansen and risk platform Chaos Labs. The methodology clustered wallets by shared funding sources within a 24-hour window (tightened to a single hour), low transaction counts, capped transaction volume, and activity routed through the same bridges. Clusters of five or more addresses were treated as statistically significant, and the largest single cluster contained 2,051 wallets. LayerZero paired the analytics with a self-report bounty that let farmers claim a reduced allocation instead of being fully excluded, and it ultimately filtered roughly 803,000 wallets from its initial snapshot.
ether.fi worked with Chaos Labs on a complementary approach centered on synchronized behavior. Using multi-line time-series analysis, the team flagged wallet clusters whose deposit and withdrawal amounts landed within roughly 5% of each other, with entry and exit times closely aligned — a signature of coordinated, scripted movement rather tha users. Flagged addresses were given a five-day window to prove they were not part of a Sybil cluster before losing eligibility.
The lesson from both: coordination is the tell. Operators can vary any one signal, but keeping funding, timing, and behavior all independent across thousands of wallets is expensive and error-prone.
Why Single-Chain Snapshots Miss Cross-Chain Farmers
Most snapshot-based detection reads one chain at a time — a Merkle snapshot of balances or activity on a single network at a single block. That is a structural blind spot.
A ring that looks like unrelated wallets on Arbitrum may reveal itself the moment you add Optimism, Starknet, Linea, and the bridges between them. The shared funding wallet, the identical bridging cadence, and the repeated interaction with the same handful of dApps only become visible when activity is stitched together across ecosystems. Single-chain snapshots also miss the reputational context: a wallet with zero meaningful history anywhere except the target chain is a very different risk than one with years of organic multichain use. Cross-chain funding-graph analysis is what turns "looks fine here" into "obviously coordinated everywhere."
Filtering Before Distribution: Reputation Scores and Proof-of-Human ID
The most effective place to stop a ring is before tokens leave the treasury, not after. That shifts detection from a post-mortem into an eligibility gate — and it is where portable on-chain reputation changes the economics.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
An on-chain attestation can make a recorded claim available to a receiving application. Acceptance, eligibility thresholds and ecosystem scope still depend on that application. A published score is not an automatic guarantee of transparent computation, universal portability or unique-person identity.
This is what Sybil resistant means in practice: not that fake identities are impossible, but that acquiring a trusted one is costly enough that mass-producing them stops being worthwhile. A score that reflects genuine, long-term, cross-chain behavior can't be spun up on demand the week before a snapshot.
The Economics: Why Airdrop Farming Persists
Farming persists because the math still works. When a token launch can distribute five, six, or seven figures of value, the marginal cost of one more wallet — gas, a few dollars of bridged capital, a slot in a script — is trivial against the expected payout. As long as detection is imperfect and rewards are large, rings are a rational investment.
That is also why detection focuses on cost, not certainty. The goal is to make each additional fake wallet more expensive to keep undetectable — unique funding, randomized timing, aged history — until the expected return per wallet drops below the effort required. Legitimate airdrops continue to launch in 2026, and genuine participation with a single real wallet remains perfectly valid; the target is the coordinated ring, not the individual user.
Can Farmers Beat Detection? The Adversarial Reality
Detection is adversarial, and sophisticated farmers adapt. They use unique funding paths per wallet, randomized timing, residential proxies, and aged wallets bought or seasoned in advance to blur the obvious clusters. These evasions defeat naive single-signal filters.
What they do not cheaply defeat is layered, cross-chain analysis combined with humanness scoring. Randomizing timing while keeping funding unique across thousands of wallets is slow and capital-intensive; faking a deep, organic, multichain history is even harder because it must be built over real time. So the honest framing is not "detection is solved" but "detection makes evasion expensive." Portable on-chain reputation raises that cost further, moving the equilibrium toward genuine users without pretending fraud can be eliminated.
Multi-accounting detection beyond airdrops
Multi-accounting detection asks whether accounts share control or eligibility-relevant activity. The same investigation appears in referral programs, loyalty rewards and marketplace promotions. Common funding or a repeated device can identify a cluster, but the program's terms determine whether the relationship is prohibited.
Join each account to the benefit it received and preserve the evidence observed before payout. Review shared households, teams and custodial infrastructure separately. A plausible cluster is a hypothesis to test; it is not a verified count of unique humans or an automatic reason to reject every member.
For implementation context, see multi-accounting prevention workflow and account-linking implementation guide. Related editorial sources include Medium comparison of airdrop fraud-prevention tools, Medium guide to multi-accounting in online gambling. Read next: what is a sybil attack crypto, click farm ad fraud detection.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best Multi-Accounting Detection Tools in 2026.
Frequently Asked Questions
Is airdrop farming illegal? Airdrop farming itself is not illegal in most jurisdictions; it is a gray-area growth-hacking activity. What projects prohibit in their terms is Sybil farming, running many wallets to claim a single person's outsized share of an allocation. Projects routinely disqualify and claw back tokens from detected rings, and large-scale coordinated fraud can draw legal scrutiny.
How do projects detect airdrop Sybils? Projects combine on-chain funding-graph analysis (tracing many wallets back to one CEX or bridge source), temporal and behavioral clustering (identical interaction sequences and synchronized timing), and reputation or humanness scoring. Analytics firms such as Nansen, Chaos Labs, and TrustaLabs use graph mining plus behavior analysis to flag coordinated clusters before or after the snapshot.
How many wallets count as a farming ring? There is no fixed threshold; a ring is defined by coordination, not a raw wallet count. In practice, detection tools flag clusters of five or more wallets that share funding and behavior. LayerZero identified clusters as large as 2,051 wallets, while ether.fi flagged wallets whose deposits and withdrawals landed within about 5% of each other with closely aligned timing.
Can farmers beat airdrop Sybil detection? Sophisticated farmers use unique funding paths, randomized timing, and residential proxies to evade filters, but cross-chain funding-graph analysis and humanness scoring still surface coordinated behavior a single-chain snapshot would miss. Detection is adversarial: layered on-chain reputation makes evasion expensive and slow rather than impossible.
What is an airdrop farming ring? An airdrop farming ring is a single operator or team funding and scripting hundreds to thousands of wallets to multiply one airdrop allocation. It is a coordinated multi-accounting, or Sybil, attack that dilutes rewards for genuine users and skews token distribution toward the operator.
What is the difference between airdrop farming and a Sybil attack? Airdrop farming is any activity aimed at qualifying for token rewards; it can be legitimate when done with a single genuine wallet. A Sybil attack is the abusive form: one entity operating many fake identities (wallets) to capture a disproportionate share. Every farming ring is a Sybil attack, but a solo farmer with one wallet is not.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] multi-accounting prevention workflow — vendor product scope.
[2] account-linking implementation guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for multi-accounting detection tools
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs documentation: hre.multi_account.changed | Verify the endpoint, event or data model against the current version before writing enforcement code. |
| ShieldLabs documentation: High-Risk Events | Read the provider definition and identify what its result establishes and what remains uncertain. |
| ShieldLabs documentation: Multi-accounting | Relate this scenario to the application action, qualification rule and later outcome record. |
| The 10 best multi-accounting detection tools in 2026 | Background on What is multi-accounting detection?. Verify implementation details in the primary references. |
| Detecting Device Farms Behind Fake Web Accounts | Background on What does a device farm look like in web account abuse?. Verify implementation details in the primary references. |
| How to prevent multi-accounting and stop fraud | Background on What is multi-accounting?. Verify implementation details in the primary references. |
| High-risk event detection. | Read the provider-stated product or use-case scope; verify the selected integration before applying a policy. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


