
Account Sharing Detection: Seats, Sessions and Token-Gated Access
Account Sharing Detection: Seats, Sessions and Token-Gated Access. Compare evidence, practical controls and limitations, with related implementation sources.
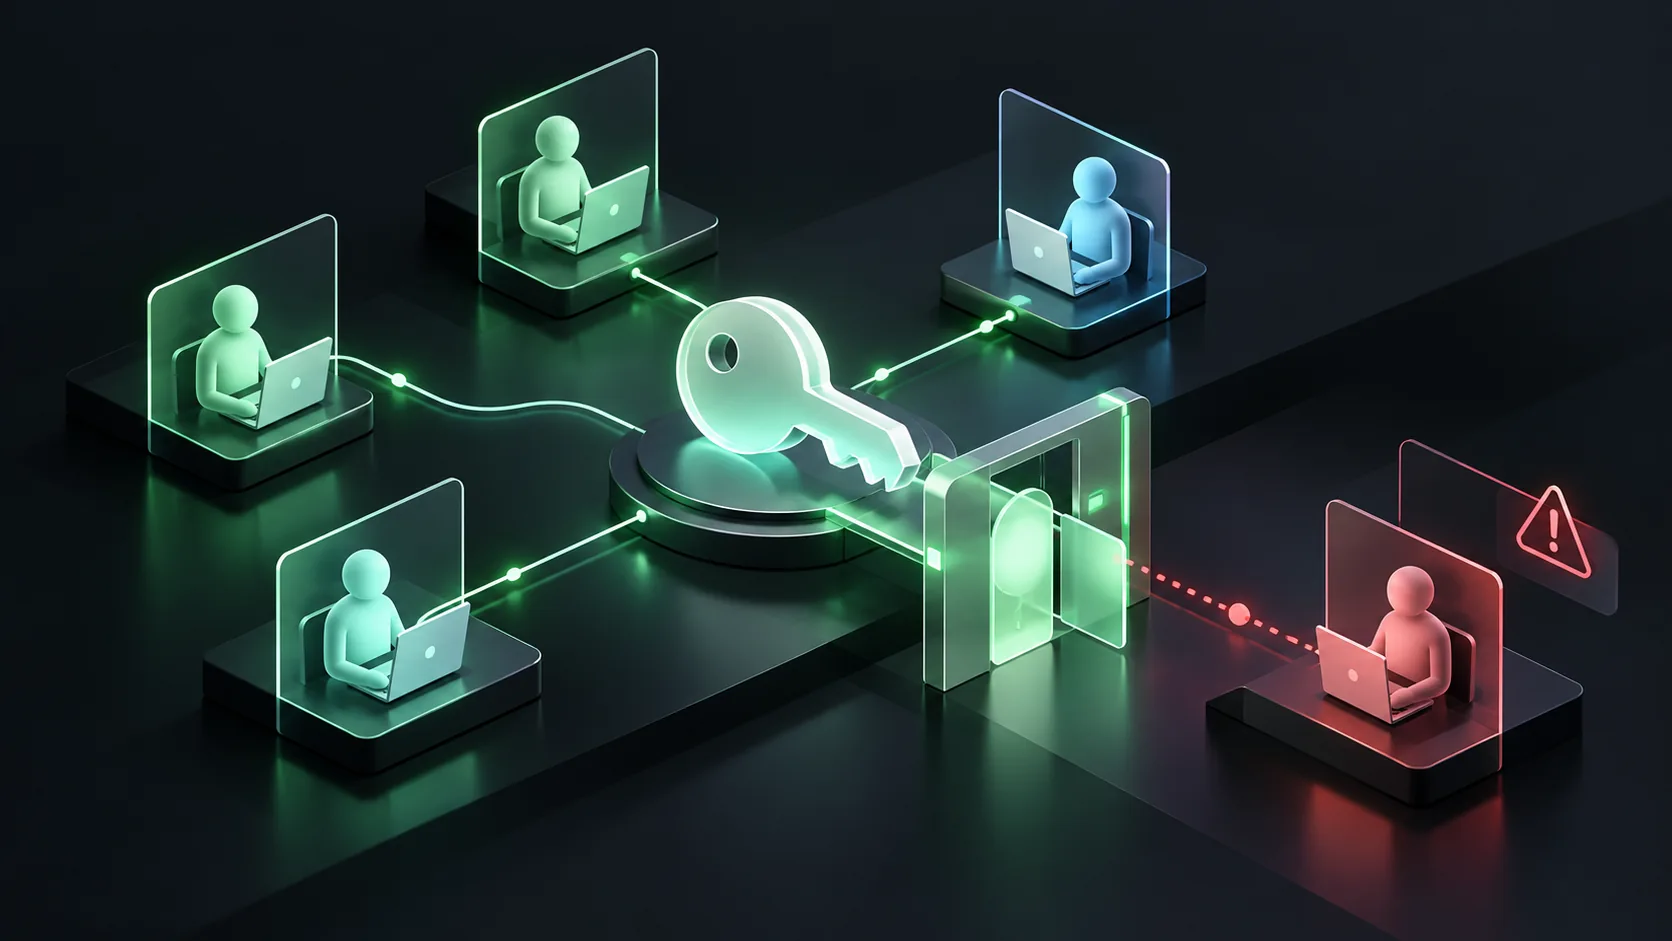
Account sharing detection reviews whether use of an account exceeds its permitted users or seats. Device relationships, session history and entitlement rules provide context, but multiple devices do not prove a violation. SaaS subscriptions and token-gated products need a policy that distinguishes legitimate shared use, paid-seat expansion and compromised accounts.
What Is Account Sharing Detection in Web3?
Account sharing detection in Web3 is the process of identifying when a single wallet, seed phrase, or token-gated login is operated by more than one person. It blends on-chain activity analysis with off-chain device and session signals to flag pooled, rented, or delegated access that breaks the one-human, one-identity assumption most protocols rely on.
In traditional apps an identity is a username and password. In Web3 it is a cryptographic keypair, so "who controls this wallet" is never obvious from the chain alone. Detection therefore asks a harder question: how many distinct humans sit behind one address?
How Wallet and Account Sharing Actually Happens in Token-Gated Ecosystems
Wallet and account sharing happens whenever several people control the same on-chain identity. In token-gated ecosystems it usually takes three forms: handing over a seed phrase outright, granting programmatic wallet delegation, or pooling a token-gated login so multiple users clear the same Collab.Land or Guild.xyz gate with one qualifying asset.
Each vector has a different risk profile:
- Seed phrase sharing grants total, irreversible control and is the most dangerous.
- Wallet delegation through scoped registries like delegate.xyz assigns limited rights without exposing the master key.
- Pooled logins let a group rent one holder's NFT or token to unlock a role, a Discord channel, or a whitelist meant for a single member.
Multisig wallets and account abstraction (ERC-4337) further blur the picture, since one address can legitimately have many signers. That is exactly why detection must read behavior, not just keys.
Why Shared Wallets Quietly Distort DAO Governance
Shared wallets distort DAO governance by hiding real voting power behind a single address. When one wallet is operated or delegated by several parties, or when a whale pools tokens through cooperating accounts, Snapshot proposals and on-chain votes stop reflecting the number of independent humans and start reflecting concentrated, disguised influence.
This quietly undermines the premise of token-weighted governance. A proposal that looks like broad consensus may be a handful of coordinated operators. Detecting shared and delegated control is what lets a DAO tell genuine participation from manufactured quorum.
How Account Sharing Skews Airdrops, Quests, and Per-User Limits
Account sharing skews airdrops and quests by letting one operator collect rewards meant for many separate humans, or by letting many humans drain a limit meant for one. Both patterns defeat per-user caps, inflate participation metrics, and route tokens to farmers instead of the real users a program is designed to reward.
The scale is documented. In its 2024 ZRO airdrop, cross-chain protocol LayerZero published a preliminary list of 803,093 wallet addresses flagged as potential sybils, narrowed down from the more than two million addresses it had initially flagged. Source: https://crypto.news/layerzero-spots-800k-sybil-addresses-airdrop-scheme/
Earlier, in May 2022, Optimism removed 17,000 addresses tied to airdrop farming and recovered more than 14 million OP for redistribution. Source: https://x.com/Optimism/status/1528830231322165249
Account Sharing vs. Sybil Attacks: Where They Overlap and Differ
Account sharing and sybil attacks overlap but invert each other. A sybil attack is one human running many wallets to multiply rewards or votes; account sharing is many humans running one wallet or login. Both break per-user fairness, and both are caught by combining on-chain activity signals with device and session data.
| Dimension | Account Sharing | Sybil Attack |
|---|---|---|
| Core pattern | Many humans, one identity | One human, many wallets |
| Primary goal | Bypass per-user limits, pool roles | Multiply airdrops, votes, rewards |
| Typical vector | Shared seed phrase, delegation, pooled login | Scripted wallet farms, single funder |
| Governance impact | Hides concentrated voting power | Fabricates fake consensus |
| Detection anchor | Concurrent sessions, device overlap | Funding graphs, timing clusters |
On-Chain Signals That Reveal Shared Wallet Access
On-chain signals reveal shared access by exposing behavior that a single human operator could not plausibly produce. Common tells include funding from a shared source, synchronized transaction timing, overlapping counterparties, and activity that fires across several chains at once. Read together, these signals separate coordinated or pooled control from an ordinary individual user.
Analysts watching for shared or sybil-farmer wallets typically weigh:
- A common funding origin, such as one centralized-exchange withdrawal seeding many wallets.
- Coordinated or near-simultaneous transactions that no single person could execute manually.
- Overlapping contract interactions and repeated counterparties across a wallet cluster.
- Behavioral shifts mid-lifecycle, where one address suddenly acts like a different operator.
- Low activity diversity and templated patterns, the classic signature of a sybil farmer.
Device and Session Signals: Lessons Token-Gated Web3 Can Borrow From Web2
Device and session signals catch sharing that the chain cannot see. When a token-gated login is opened from multiple distinct devices, IP geographies, or concurrent sessions, that mismatch points to pooled access. Web2 subscription platforms solved this problem years before Web3 inherited it, and the same telemetry transfers cleanly to gated dApps.
Netflix, for example, infers a household using IP address, device identifiers, and account activity, then challenges logins that fall outside it. Riot Games flags account sharing in League of Legends through hardware and login-pattern anomalies. Token-gated Web3 can adapt these same detections: correlate concurrent sessions, device fingerprinting, and geography against a wallet's on-chain history to reveal one login serving many operators.
Rather than reinventing this from scratch, protocols can lean on established account-sharing detection playbooks refined in web2 subscription apps and fuse them with wallet-level context that no streaming service ever had.
Proof-of-Human ID and On-Chain Reputation as a Per-Human Detection Layer
Proof-of-human identity and on-chain reputation add a per-human layer that pooled or rented wallets struggle to fake. Instead of trusting a raw address, a protocol checks whether one real, active human stands behind it. This turns detection from a wallet count into a humanness signal, which is far harder for shared or farmed accounts to imitate.
RubyScore's Multichain Reputation Score normalizes recorded wallet activity to a 0–1000 scale. Its Proof-of-Human ID is an ecosystem-specific, non-transferable attestation earned against locally defined activity thresholds. These are activity-based eligibility signals; they do not independently establish legal identity, unique personhood or honest intent.
Is Account Sharing Against the Rules in Web3?
Account sharing is rarely illegal, but it usually violates program rules. Sharing your own wallet is your right; renting, reselling, or pooling token-gated access to defeat per-user limits breaks the terms of most airdrops, quests, and gated communities. Enforcement, not legality, is the real constraint, and it depends on reliable account sharing detection.
Because on-chain terms are hard to police manually, programs increasingly encode anti-pooling rules and back them with detection plus clawbacks, as LayerZero and Optimism both demonstrated when they excluded flagged wallets after distribution.
Best Practices for Protocols to Detect and Mitigate Shared Access
Best practice is to combine layers rather than trust any single signal. Pair on-chain reputation with off-chain device and session data, require proof-of-human checks at high-value gates, prefer scoped delegation over seed-phrase handoff, and weight votes and rewards by verified humans. No one signal is decisive, but layered detection makes shared access expensive to hide.
A practical checklist for protocol and DAO teams:
- Fuse on-chain reputation scoring with device fingerprinting and session monitoring.
- Gate claims and governance votes behind a proof-of-humanity crypto check.
- Push users toward scoped delegation (delegate.xyz) and multisig instead of sharing a seed phrase.
- Rate-limit and monitor concurrent sessions on token-gated logins via Collab.Land or Guild.xyz.
- Publish explicit anti-pooling terms and enforce clawbacks on flagged wallets.
- Weight airdrops, quests, and rewards by per-human reputation, not raw wallet count.
Account sharing detection for SaaS seats and subscriptions
Account sharing detection also applies to SaaS seats, media subscriptions and paid research access. The useful unit is an account entitlement and its permitted users. Multiple devices can be legitimate, so investigate concurrent use, session history and the subscription policy before changing access.
Keep authentication and entitlement enforcement on the server. A returning-device result can support review, but it must not expose one customer's private content to another inferred user. For a subscription business, an upgrade invitation may be more appropriate than a ban when sharing is allowed under a different plan.
For implementation context, see account-sharing controls and account-sharing investigation guide. Related editorial sources include Medium guide to detecting seat sharing in SaaS. Read next: fraud prevention workflows, best device fingerprinting solutions 2026.
Compare tools for this workflow
For a documented shortlist and a provider-selection checklist, read 7 Best Free Trial Abuse Prevention Tools in 2026.
Frequently Asked Questions
What is account sharing detection in Web3? Account sharing detection in Web3 is the process of spotting when a single wallet, seed phrase, or token-gated login is controlled by multiple people. It combines device fingerprints, session behavior, and on-chain activity patterns to flag shared access that undermines per-user limits, airdrop distribution, and DAO voting.
Is sharing a crypto wallet or seed phrase safe? Sharing a seed phrase is never safe: anyone who holds it gains full, irreversible control of the wallet and its assets. Safer alternatives are scoped on-chain delegation standards or multisig wallets, which grant limited, revocable access without exposing the master key.
How do DAOs detect shared or delegated wallet access? DAOs detect shared access by correlating on-chain signals such as common funding sources, synchronized voting, and overlapping transaction timing with off-chain device and session data. On-chain reputation scores and proof-of-human checks add a per-human layer that pooled or rented wallets struggle to imitate.
Does account sharing count as a sybil attack? Account sharing and sybil attacks overlap but are not identical. A sybil attack uses many wallets controlled by one person to multiply rewards or votes, while account sharing is many people operating one wallet or login. Both break per-user fairness and are caught with combined on-chain and device signals.
Is account sharing against airdrop and quest rules? Most airdrop, quest, and token-gated programs prohibit pooling, renting, or reselling access in their terms, and violators are routinely excluded or clawed back. Enforcement depends on account sharing detection that ties each wallet to a single human through reputation, device, and behavioral signals.
What signals reveal that a wallet is being shared? Signals of a shared wallet include multiple distinct devices or IP geographies on one account, concurrent logins, mismatched session behavior, funding from a shared exchange withdrawal, and on-chain activity patterns that are inconsistent with a single human operator acting over time.
Sources and editorial notes
Updated in 2026 by RubyScore Research, the organizational editorial byline for this blog. Product descriptions are attributed to their publishers; examples and risk signals do not establish a shared vendor benchmark. Disclosure: linked ShieldLabs publications and related comparison sites are part of the project portfolio. For source-specific corrections, contact RubyScore.
[1] account-sharing controls — vendor product scope.
[2] account-sharing investigation guide — related technical or workflow explanation.
[3] RubyScore documentation — on-chain product context.
Further sources for account sharing detection
These references cover specific parts of the workflow discussed above. Provider explanations, product pages, documentation and controlled demos have different evidential roles; the notes state how each source should be used.
| Source | How to use it in this workflow |
|---|---|
| ShieldLabs demo: Account Sharing Prevention Test | Inspect this controlled workflow example; do not treat a demo as a production accuracy benchmark. |
| ShieldLabs demo: Paywall Bypass Prevention Test | Inspect this controlled workflow example; do not treat a demo as a production accuracy benchmark. |
| ShieldLabs documentation: Account sharing | Use the scenario to plan an integration test; a published example is not a test result from your application. |
| ShieldLabs documentation: Paywall enforcement | Use the scenario to plan an integration test; a published example is not a test result from your application. |
| ShieldLabs documentation: Account sharing | Relate this scenario to the application action, qualification rule and later outcome record. |
| ShieldLabs documentation: Paywall enforcement | Relate this scenario to the application action, qualification rule and later outcome record. |
| Seat sharing in SaaS: how to detect it and turn sharers into seats | Background on What is seat sharing in SaaS?. Verify implementation details in the primary references. |
| Fraud prevention for media. | Read the provider-stated product or use-case scope; verify the selected integration before applying a policy. |
| Paywall bypass prevention. | Read the provider-stated product or use-case scope; verify the selected integration before applying a policy. |
Filtering bots before your next campaign?
RubyScore filtered 500,000+ bots for Somnia and 243,000+ for Linea using on-chain reputation and Proof-of-Human ID.
Get Score


